ChatGPT Google Drive Permissions: Workspace Security and Access Scopes
ChatGPT Google Drive permissions represent the specific OAuth 2.0 authorization scopes granted to OpenAI to index, read, or search documents within a user's Google Drive. Managing access requires configuring identity scopes, Google Workspace administrator policies, and document boundaries. When native integrations encounter domain blocks or rate limits, organizations bridge documents into indexed cloud workspaces via remote Model Context Protocol servers.

How ChatGPT Google Drive OAuth Scopes and Permissions Work
Connecting ChatGPT to Google Drive exposes a direct tension between conversational utility and organizational information governance: while users expect to search a single document, the OAuth 2.0 authorization grant provides the application with broad authority to read and extract files across their entire storage repository.
ChatGPT Google Drive permissions represent the specific OAuth 2.0 authorization scopes granted to OpenAI to index, read, or search documents within a user's Google Drive. Most organizations maintain their operational assets in Google Drive, Dropbox, OneDrive, Box, or SharePoint. Engineering plans, financial spreadsheets, research memos, and client agreements live across personal folders and Shared Drives. When connecting ChatGPT or custom agentic workflows to these repositories, users expect immediate conversational access. Instead, they frequently encounter authentication loops, permission rejections, and administrative blocks.
The OAuth 2.0 Scope Architecture
OpenAI's Google Drive integration relies on Google's standard OAuth 2.0 identity and authorization protocols. When a user initiates a connection from ChatGPT on the web or the desktop interface, Google presents an OAuth consent screen requesting access to their Google account. Under the hood, the connector requests specific access scopes:
https://www.googleapis.com/auth/drive.readonly: Grants permission to search for files, inspect directory structures, view file metadata, and read document bodies. ChatGPT uses this scope to retrieve document text and supply context for conversational prompts.https://www.googleapis.com/auth/drive.metadata.readonly: Grants permission to view file metadata without downloading file bodies. This scope allows the application to list folder hierarchies, file names, modification dates, and MIME types.https://www.googleapis.com/auth/userinfo.emailandhttps://www.googleapis.com/auth/userinfo.profile: Grants access to the user's primary email address and basic profile information to link the Google identity to the active ChatGPT account.
Understanding the boundary of these scopes clarifies what the model can and cannot perform. The drive.readonly scope allows ChatGPT to inspect files and extract text, but it does not grant administrative authority over the Google account. The native integration does not request the full read-write drive scope or the application-specific drive.file scope. Consequently, ChatGPT cannot rewrite, modify, overwrite, or delete company files stored in Google Drive. Its native connection functions strictly as a read-only retrieval bridge.
Delegated User Authority and Data Exposure Risks
ChatGPT operates strictly under delegated user authority. The model inherits the exact permissions of the individual employee who authenticates the OAuth session. If a team member lacks access to a restricted finance directory in Google Drive, ChatGPT cannot discover or retrieve documents from that location.
However, delegated authority creates serious data boundary risks when applied broadly. If an employee possesses read access to sensitive customer records, executive compensation sheets, or confidential product roadmaps, granting ChatGPT read access allows the model to ingest those files whenever referenced in prompts. Restricting access to scoped workspace folders prevents inadvertent exposure of executive or confidential files across conversational sessions.
Related guides
- Setting Up Rclone Google Drive OAuth for Headless Scripts and AgentsRclone Google Drive OAuth is the token-based authorization handshake allowing rclone to access user files and Shared...
- How to Configure AI Agent Granular PermissionsGranular permissions are the defense layer between an autonomous AI agent and your sensitive data. With identity...
- Agentic AI Security Risks: Threats, Vulnerabilities, and MitigationsAI agents that can plan actions, call tools, and access files introduce security risks that go well beyond prompt...
- Google Drive Folder Permissions: Structuring Access and Subfolder SharingGoogle Drive folder permissions are access control rules assigned at the directory level that dictate whether users or...
- How to Prevent Tool Poisoning Attacks on AI AgentsTool poisoning is an attack where a malicious MCP server or tool registry provides manipulated tool descriptions or...
- Why Google Drive Version History Fails for Autonomous AgentsGoogle Drive version history is designed for human editing, but it fails when autonomous agents write to files at high...
More on this subject: Agent Security and Governance (65 guides)
How Google Workspace Admins Control ChatGPT Drive Access
Default Google Workspace security blocks unverified third-party apps from accessing Drive data until an administrator explicitly allows the client ID. When an employee on a managed business domain attempts to link Google Drive to ChatGPT, Google halts the authentication flow and displays an administrative block screen: "Access blocked: your institution's admin needs to review this app."
This response indicates an active security policy rather than a service failure. Google Workspace provides centralized API access controls to prevent unapproved external applications from extracting corporate files. Resolving this access block requires administrative configuration within the Google Admin Console.
Step-by-Step Google Workspace Admin Configuration
If you manage your organization's Google Workspace domain, follow these steps to review and approve the ChatGPT application:
- Sign in to the Google Admin console at
admin.google.comusing a Super Administrator account with Service Settings privileges. - In the left navigation menu, go to Security, select Access and data control, and click API controls.
- In the App access control section, click Manage Third-Party App Access.
- Click Add app, then select OAuth App Name or Client ID from the dropdown menu.
- In the search box, enter
ChatGPTor paste OpenAI's official OAuth client ID, then click Search. - Select the application from the search results.
- Choose the organizational scope: apply the access setting to the top-level root organization or restrict it to specific Organizational Units.
- Under the access policy settings, choose the appropriate access classification:
- Trusted: The app can access all Google Workspace services, including Drive, Docs, Sheets, and Slides data requested by its OAuth scopes.
- Limited: The app is restricted from accessing sensitive data scopes, blocking deep Drive reads while permitting basic identity sign-in.
- Blocked: The app is completely prevented from accessing Google Workspace data.
- Click Save to confirm the policy.
Policy propagation across Google's distributed data centers is asynchronous. While administrative changes take effect immediately in the console, domain-wide distribution can take up to twenty-four hours, though user connections frequently succeed within fifteen minutes.
Scoping by Organizational Unit
Applying a blanket "Trusted" status across the entire corporate domain creates unnecessary exposure. Google Workspace supports Organizational Unit (OU) policy inheritance. Administrators can place technical teams, product analysts, and marketing specialists into a dedicated Organizational Unit and enable the ChatGPT integration exclusively for that group.
Departments handling sensitive records, such as Legal, Finance, and People Operations, remain in restricted Organizational Units where unapproved third-party API access remains blocked. If an employee in Finance attempts to connect Google Drive, the domain policy continues to block the request.
Auditing Accessed Apps and Token Lifecycles
Google Workspace administrators should regularly audit external connections. Under API controls, the Accessed apps tab lists all third-party tools that users have authenticated. Administrators can review the number of active users, inspect the specific Google service APIs and OAuth scopes requested, and download a CSV report detailing access across organizational units.
How to Restrict Boundaries Across Shared Drives and DLP Policies
Even after domain administrators approve the ChatGPT OAuth application, users frequently encounter 403 Forbidden errors or missing file errors when attempting to query specific folders. These issues almost always stem from the structural differences between personal "My Drive" storage and corporate Google Shared Drives.
Shared Drive Role Hierarchies and API Export Errors
Personal Google Drive folders belong to individual accounts, where the owner controls sharing settings. In contrast, Google Shared Drives belong to the organization and enforce a five-tier permission hierarchy: Manager, Content Manager, Contributor, Commenter, and Viewer.
When ChatGPT reads files from Google Drive, it interacts with Google's backend export endpoints to convert proprietary formats (Docs, Sheets, and Slides) into readable text streams. Shared Drive managers can enable a restrictive governance toggle: "Restrict download, print, and copy for commenters and viewers."
When this restriction is active, Google's API rejects export requests initiated by commenters or viewers. The user can read the document in a web browser, but ChatGPT's API call fails with an access denied error. To resolve this without lowering general drive security, administrators must adjust the Shared Drive permissions or move the target reference files into an accessible workspace repository.
Data Loss Prevention (DLP) Policies
Google Workspace Enterprise editions allow administrators to deploy automated Data Loss Prevention (DLP) rules. DLP systems scan documents stored in Google Drive for sensitive content, including credit card numbers, tax identifiers, medical records, and confidential source code strings.
When a DLP rule flags a document, Google Drive automatically restricts external sharing and API exports. Even if an employee explicitly selects a flagged document in ChatGPT, the platform cannot download the content. Organizations use DLP rules alongside organizational unit controls to enforce compliance guardrails without relying on manual employee discretion.
Dual-Gate Governance in ChatGPT Team and Enterprise
In corporate environments, access control operates across two administrative domains. Authorizing ChatGPT in Google Workspace is only the first requirement. If your company uses a ChatGPT Team or Enterprise plan, a ChatGPT workspace administrator must also enable third-party connectors inside OpenAI's admin settings.
Workspace owners navigate to the Admin Panel, select Connected Apps, locate Google Drive, and toggle availability for organization members. Until both Google Workspace and ChatGPT workspace settings are active, end-user connection attempts will fail.
Revoking Permissions and Terminating Active Tokens
When an employee changes roles, leaves the company, or suspects credential compromise, organizations must revoke OAuth grants immediately:
- User-Level Disconnection: In ChatGPT, open Settings, select Connected Apps, find Google Drive, and click Disconnect. To clear cached tokens completely, navigate to Google Account settings at
myaccount.google.com/permissions, locate ChatGPT, and select Delete all connections. - Admin-Level Token Revocation: In the Google Admin console, open the user's account profile under Directory > Users. Open the Security section and select Connected applications. Administrators can revoke the specific ChatGPT refresh token or wipe all active OAuth application tokens with a single click.
Why Native Cloud Storage Connectors Hit Retrieval Bottlenecks
Troubleshooting OAuth permissions often reveals a deeper architectural limitation: native cloud storage connectors were designed for basic document attachment, not high-speed retrieval-augmented generation (RAG) across large file collections.
Most teams keep their operational files in Dropbox, Google Drive, OneDrive, Box, or SharePoint. When connecting conversational models or automated agent workflows to these repositories, the native connector provides a direct bridge. However, the native connector has clear boundaries in what it reaches and where it becomes slow or partial.
Whole-Document Extraction and Context Saturation
The native ChatGPT Google Drive connector does not maintain a continuous vector index of an organization's files. Instead, it extracts document text on demand. When a user references a file or mentions Google Drive in a prompt, the integration downloads the entire text payload over Google APIs and injects it directly into the prompt context window.
This approach introduces severe operational penalties:
- Context Window Saturation: Injecting full documents consumes thousands of tokens per conversational turn. When working with multi-page agreements or detailed technical manuals, context limits are reached rapidly.
- Attention Dilution: Large language models experience diminished accuracy when required to locate specific facts inside massive prompt payloads. Key contract clauses or financial figures can be overlooked when surrounded by hundreds of pages of unindexed text.
- Latency Overhead: Downloading large files over external REST APIs on every query adds substantial delay before the model can begin generating an answer.
- Visual and Tabular Blind Spots: Native text extraction discards visual formatting, embedded schematics, charts, and scanned images that lack embedded OCR text layers.
API Rate Quotas and Recursive Traversal Limits
Google Drive organizes files using unique alphanumeric identifiers rather than flat file paths. To search across nested folders, native connectors must perform recursive directory listings (files.list) and multiple server-side document exports.
Under heavy research workloads, repeated API calls quickly draw down Google's per-user rate quotas, triggering HTTP 429 quota exhaustion errors. Automated workflows stall while waiting out backoff periods.
Measured Connector Performance Across Cloud Storage
Connector architecture directly affects agent execution speed, token consumption, and operational cost. The connector comparison is published at https://fast.io/benchmarks/, where Fastio was measured the fastest and the lowest cost of the providers tested.
Every measured row represents that provider's native connector in Claude Cowork across Fastio, Box, Dropbox, Google Drive, and OneDrive. SharePoint was not measured at all.
By decoupling file storage from agent retrieval, teams avoid the latency and rate-limit traps inherent in traversing unindexed REST APIs.
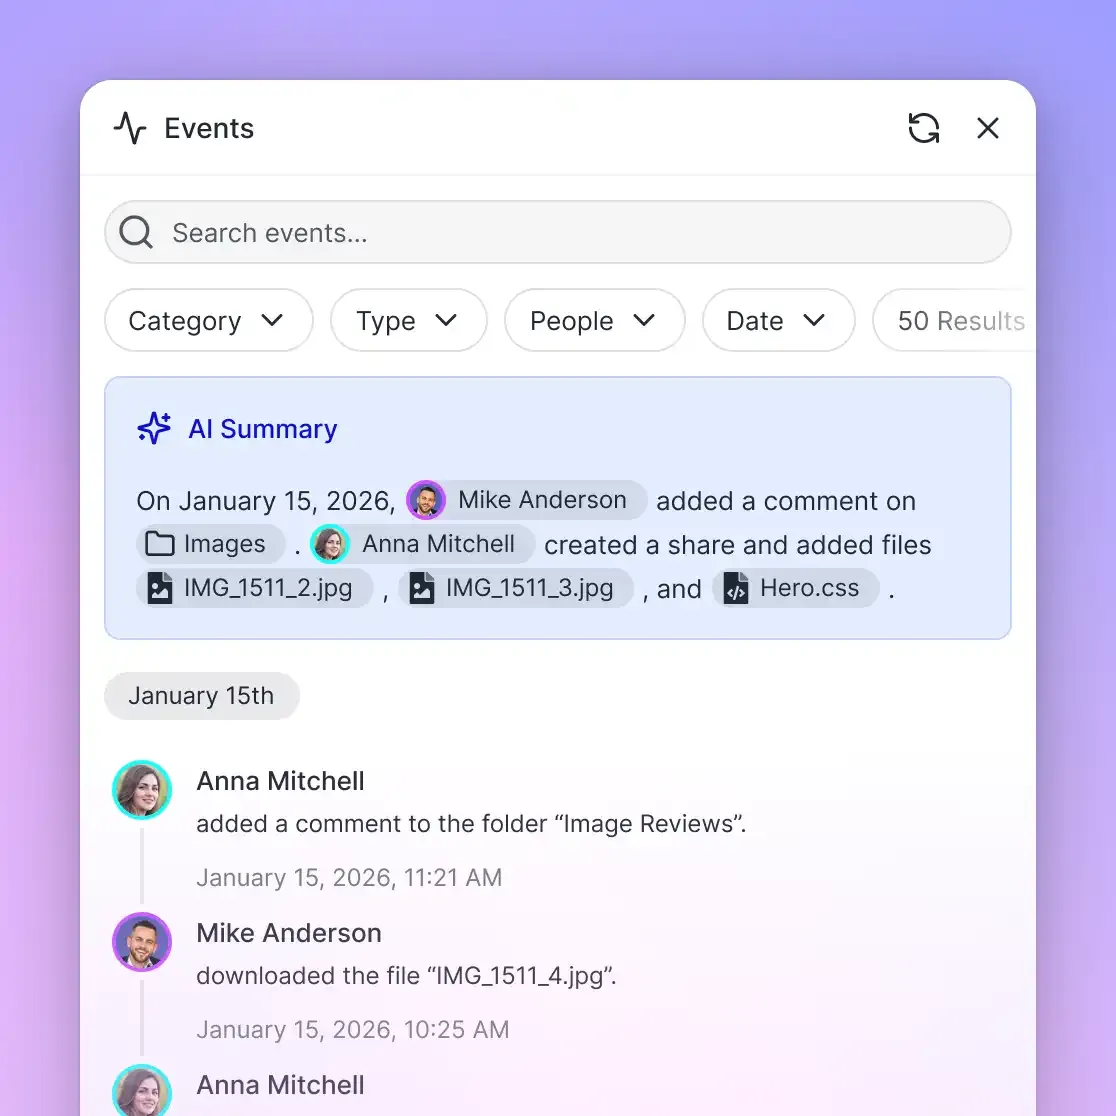


Govern AI Agent Access Across Your Cloud Documents
Connect ChatGPT to Fastio workspaces with role-based permissions, automated hybrid search indexing, and a detailed activity log of changes. Starts with a 14-day free trial.
How to Connect Google Drive to ChatGPT via Remote MCP
To eliminate permission bottlenecks, rate-limit stalls, and context window bloat, organizations adopt a two-tier storage architecture. Teams keep Google Drive as their primary authoring and collaboration environment, while Fastio provides the intelligent workspace and retrieval layer for ChatGPT and automated AI agents.
In this model, relevant Google Drive folders are imported directly into a Fastio workspace. Fastio supports cloud sync for Google Drive, Dropbox, Box, and OneDrive on a scheduled or on-demand basis. Server-to-server cloud import transfers documents directly without consuming local device bandwidth or requiring personal OAuth delegations from individual team members.
Automated Indexing with Intelligence Mode
Once documents land in a Fastio workspace, Intelligence Mode automatically indexes their contents for hybrid search. Hybrid search combines exact full-text keyword matching, dense semantic vector retrieval, and search-by-metadata-value into a single unified index.
When an agent connects through the remote MCP server, it searches the indexed files instead of pulling whole folders. ChatGPT queries the workspace index and retrieves only the precise text passages answering the question, complete with document names and citations. The conversational context remains compact, inference latency drops, and answers are verifiable against source materials.
Structured Document Extraction with Metadata Views
For complex operational files, teams configure Metadata Views. Metadata Views turn unstructured documents into a live, queryable database. Users describe the fields they want extracted in natural language (such as agreement termination dates, counterparties, contract values, or governing jurisdictions).
Fastio automatically establishes a typed schema (Text, Integer, Decimal, Boolean, URL, JSON, Date & Time), matches workspace files, and populates a filterable spreadsheet view. AI agents query Metadata Views directly via MCP tools, retrieving structured tabular data without scanning narrative paragraphs.
Connecting ChatGPT to Fastio via Remote MCP
Fastio exposes its remote Model Context Protocol server over Streamable HTTP. Teams can connect ChatGPT using two verified pathways:
- Fastio Plugin (Preferred): Open the plugin directory at
chatgpt.com/plugins, locate Fastio, select Install plugin, and sign in to Fastio when prompted. In conversations, simply mention@Fastioto query your workspaces. - Custom MCP Server (Alternative): In ChatGPT Settings, open Security and login and turn on Developer mode. Navigate to
chatgpt.com/plugins, click the plus button, name the connector Fastio, enterhttps://mcp.fast.io/mcp/operationsas the MCP server URL, and complete the connection.
Setup instructions and endpoint details are documented at https://mcp.fast.io/docs. Authentication occurs via OAuth 2.0 in the browser. During sign-in, users encounter a Review Permissions screen where they choose Read Only or Read & Write and select which organizations and workspaces the connection can reach.
Enterprise Governance and Team Workspaces
Fastio provides structured access governance that addresses the administrative challenges of personal Google Drive connections:
- Org-Owned Workspaces: Files belong to the organizational workspace rather than individual employee accounts, preventing broken integrations when personnel depart.
- Role-Based Permissions: Permissions are configured per organization, workspace, and share through member roles. Every user inside a workspace accesses assets according to their assigned role. When an organization needs to isolate specific documents or provide external access to a single folder, teams create a scoped share or a separate workspace.
- Detailed Activity Log: Fastio maintains a detailed activity log of changes, recording uploads, edits, moves, deletions, membership updates, and share creation. It does not record read-only events such as views or downloads. External shares can disable file downloads.
- Security Standards: Fastio runs on cloud infrastructure partners, including Google Cloud Platform and Cloudflare, that are certified to industry-leading security standards. Data is protected with encryption in transit and at rest.
Workspace Pricing and Setup
Monthly plans start with a 14-day free trial, which requires a credit card. Usage-based credits meter AI work, and subscriptions can be configured on our pricing page.
Sources
References used to verify factual claims in this guide.
-
Google Workspace administrators can configure third-party application policies to mark client applications as Trusted, Limited, Specific Google data, or Blocked.
Frequently Asked Questions
What permissions does ChatGPT ask for on Google Drive?
ChatGPT requests OAuth 2.0 read-only scopes when connecting to Google Drive, specifically `drive.readonly` and `drive.metadata.readonly`, alongside standard profile and email scopes. These permissions allow the model to search file titles, inspect directory hierarchies, and download document bodies for prompt context. ChatGPT does not request write or delete scopes and cannot modify, overwrite, or delete your files.
How do Google Workspace admins allow ChatGPT Drive integration?
Google Workspace administrators approve the integration by signing in to `admin.google.com`, navigating to Security > Access and data control > API controls, and opening Manage Third-Party App Access. From there, administrators search for the ChatGPT OAuth client ID and assign an access status of Trusted for the entire domain or restrict access to specific Organizational Units.
Can ChatGPT edit or delete my Google Drive files?
ChatGPT cannot edit, overwrite, or delete files in Google Drive. The native integration requests read-only OAuth scopes (`drive.readonly` and `drive.metadata.readonly`). OpenAI models cannot modify document formatting, edit spreadsheet values, or delete assets from personal storage or Shared Drives.
How can teams restrict ChatGPT access to specific Google Drive folders?
Google Drive does not offer folder-scoped OAuth grants, so connecting an account exposes all files the authenticating user can read. To restrict AI access to designated folders, organizations import target directories into a dedicated Fastio workspace, where role-based permissions and scoped shares isolate data from sensitive company repositories.
Why does Google display an access blocked screen when connecting ChatGPT?
Google displays 'Access blocked: your institution's admin needs to review this app' when a managed Google Workspace domain enforces API controls that block unverified third-party applications by default. The block screen remains active until a domain Super Administrator explicitly marks the ChatGPT OAuth client ID as Trusted or Limited in the Google Admin Console.
Can Fastio import from Google Drive?
Fastio supports server-to-server cloud import and scheduled or on-demand folder sync for Google Drive. Importing Google Drive folders into a Fastio workspace allows Intelligence Mode to index documents for hybrid search, enabling AI agents to query content via remote Model Context Protocol servers without draining Google API rate quotas.
Related Resources

Govern AI Agent Access Across Your Cloud Documents
Connect ChatGPT to Fastio workspaces with role-based permissions, automated hybrid search indexing, and a detailed activity log of changes. Starts with a 14-day free trial.