Claude Connectors Data Access: Permissions, Governance, and Safe Storage Sync
Claude Connectors data access refers to the permission boundaries, authentication protocols, and file-level scopes that govern what external data Claude can read or modify. When teams connect AI models directly to cloud drives, broad read permissions often expose entire corporate file trees. A safer governance model isolates project files in shared workspaces, synchronizes designated folders on a schedule, and lets Claude search indexed documents through scoped remote MCP connections.

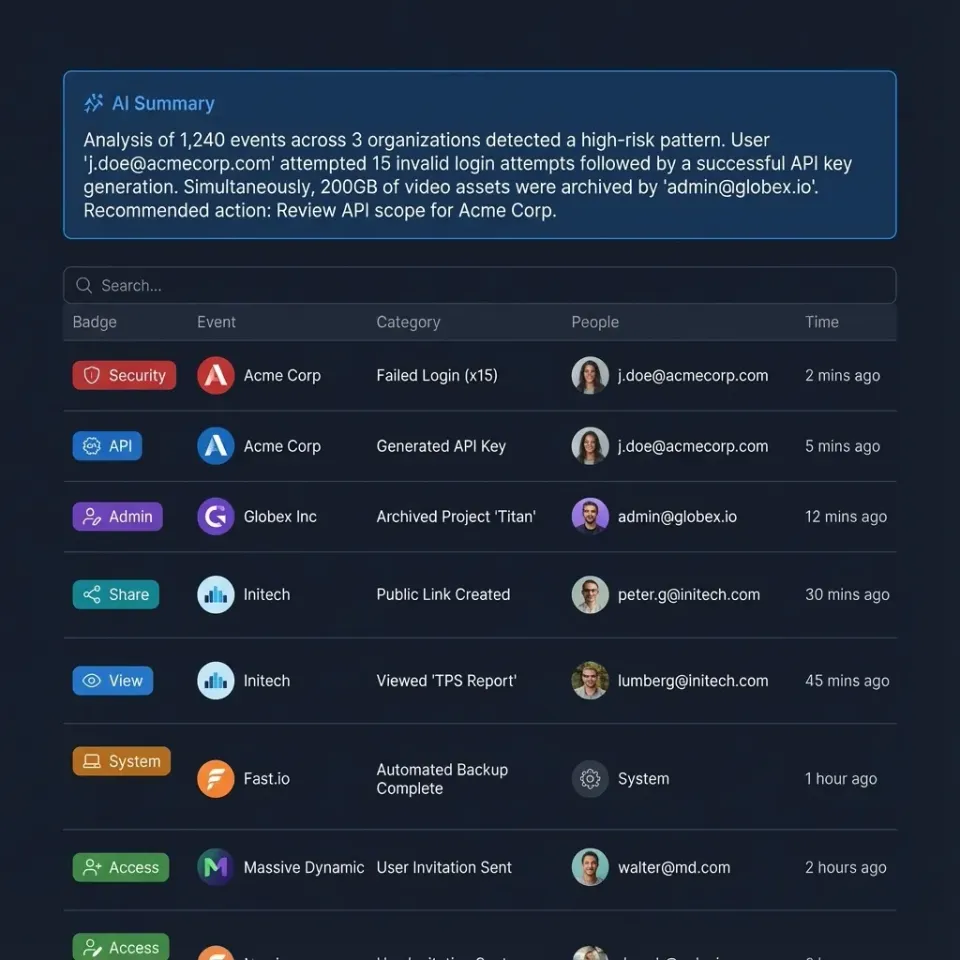
How Claude Connectors Access External Cloud Storage
When an employee connects Claude to a corporate Google Drive or OneDrive account, the OAuth prompt typically asks for read access across all files the user can reach, not just the active project folder. The AI connector inherits every permission the employee holds, creating an invisible data exposure path across financial records, internal memos, and customer data that the conversation never needed.
Claude Connectors data access refers to the permission boundaries, authentication protocols, and file-level scopes that govern what external data Claude can read or modify. Understanding how these connectors interact with underlying file systems is essential for security teams, system architects, and technical managers evaluating generative AI deployments.
Claude interacts with external systems using Anthropic's Model Context Protocol (MCP), an open standard designed to expose tools, resources, and prompts to foundation models through structured JSON-RPC messages. Connectors exist in two primary formats:
- Pre-built Cloud Connectors: Managed integrations for platforms like Google Drive, Gmail, Slack, and Microsoft 365. These operate through hosted cloud adapters where authentication uses OAuth 2.0. Once authorized, Claude issues read queries directly against vendor APIs.
- Custom Remote MCP Connectors: Dedicated servers that implement the MCP specification over Streamable HTTP. These servers expose customized tool definitions, execute scoped database queries, or connect directly to persistent cloud workspaces.
When a user submits a prompt that requires external context, Claude inspects the available tool definitions declared by its active connectors. If the user asks a question about an internal document, Claude issues a tool call containing search keywords, folder identifiers, or document paths. The connector executes this query against the storage provider API, packages the matching files or excerpts, and passes the payload back into Claude's prompt context.
The architectural challenge stems from the operational difference between human file access and automated AI ingestion. A human employee browsing Google Drive or Box clicks on individual files one by one. In contrast, an AI model executes automated search functions across entire directory trees. Because standard cloud storage OAuth grants often request broad read scopes (such as drive.readonly or Files.Read), Claude receives programmatic access to every document the authenticating user can open. If an engineer has read permissions for organizational budgets or customer agreements, Claude can surface that information during routine conversations unless structural boundaries isolate the data. Organizations evaluating safe storage layers can explore Fastio storage for agents to establish clean operational perimeters.
Related guides
- Can Copilot Access SharePoint? Permissions, Libraries, and SetupMicrosoft Copilot can access SharePoint document libraries when users hold explicit read permissions through Microsoft...
- How to Connect Clay and HubSpot for Automated Data SyncConnecting a clay hubspot integration allows teams to natively sync contact and company records without manual work....
- Claude Connectors: How AI Connectors Work and How to Connect Cloud StorageClaude Connectors are standardized integrations and Model Context Protocol (MCP) bridges that allow Anthropic's Claude...
- What Data Can Claude Access Through Connectors? How to Limit It to Specific FoldersClaude's connectors can read whatever the connected account can open in Google Drive, OneDrive, Dropbox or Box, and...
- Can Claude Access Dropbox? Native Connectors vs Workspace MCPClaude can access Dropbox files through direct chat attachments, the native Claude Cowork connector, or via remote...
- Can Claude Access SharePoint? Permissions, Security, and WorkspacesClaude cannot browse Microsoft SharePoint without administrative setup, but teams have two primary integration paths....
More on this subject: Claude and Claude Code (285 guides)
Checklist of Critical Data Access Risks in Cloud Storage Connectors
Direct cloud drive connectors often request broad tenant-level read permissions across unsegmented drives. While this provides immediate convenience for personal testing, connecting unmanaged corporate storage directly to conversational AI introduces substantial operational risks.
Here is a checklist of four primary data access risks organizations face when connecting AI models directly to corporate cloud storage, along with practical remediation steps for each:
1. Scope Inflation Across Unsegmented Drives
Most commercial cloud storage providers handle third-party integrations using tenant-level or account-wide OAuth scopes. When an employee connects Claude to Google Drive, Dropbox, Box, or OneDrive, the authorization consent screen rarely allows selecting a single folder. Instead, the connector requests access to all files within the user's corporate account.
- The Risk: The connector inherits all permissions granted to that employee identity. If company-wide folders contain unencrypted payroll sheets, legal drafts, or API credentials, the model can query and ingest those files during ordinary interactions.
- Remediation: Enforce repository segmentation before connecting AI tools. Instead of granting an AI agent access to a root corporate drive, synchronize only approved project folders into dedicated, isolated workspaces with explicitly restricted member roles.
2. Prompt Injection and Indirect Document Poisoning
Connecting Claude to shared cloud storage means the model reads untrusted text authored by diverse internal colleagues, external clients, or automated scrapers.
- The Risk: Malicious actors or compromised files can introduce indirect prompt injection attacks. A shared PDF, spreadsheet, or markdown document containing hidden instructions (such as instructing the model to ignore prior instructions and extract sensitive records) can hijack Claude's reasoning when the connector retrieves that document.
- Remediation: Enforce read-only connectors for general document exploration, isolate external document ingestion from operational prompts, and implement strict system-prompt boundary markers. Never give an AI connector write or execute permissions on drives containing unvetted third-party uploads.
3. Excessive Context Window Consumption and High Latency
Native cloud storage connectors typically fetch documents by downloading raw files or large textual blocks across standard REST APIs.
- The Prompt Cost: When Claude queries a cloud drive for a specific policy answer, naive connectors often retrieve entire multi-page documents and dump tens of thousands of tokens into the prompt context. This consumes substantial token allowances, degrades response latency, and increases inference costs.
- The Retrieval Failure: Loading massive files into context introduces the lost-in-the-middle problem, where the model misses critical details buried deep within lengthy technical reports or contracts.
- Remediation: Decouple file storage from LLM ingestion by using workspaces equipped with built-in retrieval-augmented generation (RAG) and hybrid search (combining full-text and semantic vector search). Instead of transferring entire files, the connector queries an index and injects only relevant paragraph snippets accompanied by exact citations.
4. Write Tool Ambiguity and Unintended File Modifications
Some advanced connectors and agent frameworks request write permissions to update documents, save meeting summaries, or reorganize directory structures.
- The Risk: Language models operate probabilistically. If an ambiguous user instruction or hallucinated function argument triggers a write tool, the model can overwrite existing files, delete critical folders, or scramble file naming conventions. Standard cloud drives often lack granular agent activity records, making post-incident investigation difficult.
- Remediation: Apply strict role-based separation between read tools and write tools. For agent integrations that require file creation, use persistent workspaces with per-file version history where every write is captured as a distinct, restorable version. Ensure the storage platform maintains a detailed activity log tracking every change made by people and agents alike.
Claude Connectors Data Privacy and Model Training Policies
Data privacy is the first concern enterprise security teams evaluate before enabling AI connectors. When Claude reads documents from Google Drive, OneDrive, or an internal MCP server, organizations must know whether proprietary data is stored by Anthropic, inspected by human reviewers, or used to train future foundation models.
Anthropic maintains distinct data handling standards depending on whether an account operates under Consumer Terms or Commercial Terms:
- Consumer Plans (Claude Free, Pro, and Max): Users on consumer tiers are provided settings to control whether their conversation history and attached data can be used for model training and product improvement. By default, users can opt in or opt out of training in their account settings.
- Commercial Plans (Claude Team, Claude Enterprise, Claude for Government, and Claude for Education): Accounts operating under Anthropic's Commercial Terms of Service are completely excluded from model training. Anthropic does not use prompts, completions, or connector-retrieved documents from commercial accounts to train its models. The same strict exclusion applies to developers accessing Claude through API endpoints on Amazon Bedrock or Google Cloud Vertex AI.
When evaluating connectors specifically, Anthropic's privacy documentation outlines clear boundaries regarding external tools and MCP servers. Raw content retrieved dynamically from an external connector or remote MCP server is not used for model training. The only scenario where connector-derived information enters the training corpus on consumer accounts is when a user explicitly copies text from a connector response and pastes it directly into a standard prompt input, or submits conversation logs through user feedback forms.
Permission inheritance is another foundational governance principle. According to the official Claude Connectors documentation: "Claude inherits each person's permissions from the connected service. If someone can't access a specific file, channel, or record in the source system, the connector can't reach it from Claude either."
While inherited access prevents an employee from reading documents they cannot normally access, it does not solve internal over-permissioning. If an enterprise cloud drive suffers from permissive link sharing (such as folders set to allow viewing across the entire organization), Claude inherits that broad visibility. A junior employee who prompts Claude to summarize executive meeting notes will receive those notes if the underlying Google Drive or Box folder was improperly configured with org-wide read permissions.
For organizations running Claude Enterprise or Team plans, administrators gain centralized governance controls. Administrators can enable or disable connectors globally, mandate which pre-built integrations are accessible to users, restrict connections to approved external domains, and review connector status across active workspaces.
The Safe Storage Architecture: Workspace Isolation and Scheduled Sync
Most articles discussing Claude connectors focus purely on connecting personal drives, ignoring how real teams manage storage and governance. The reality in enterprise environments is that teams already keep their primary files in Google Drive, Dropbox, Box, or OneDrive. Asking employees to abandon existing cloud drives is unrealistic; asking security teams to open those drives directly to broad AI read scopes is unacceptable.
Native cloud drive connectors create a difficult tradeoff. Pointing Claude directly at a corporate Google Drive or OneDrive root folder leads to slow folder scans, API rate throttling, excessive token burn, and uncontrolled data visibility.
A safer architecture decouples the primary corporate drive from the AI integration layer by introducing an isolated workspace. In this pattern, teams keep their existing cloud storage as the system of record. Designated project folders synchronize into an isolated Fastio workspace, and Claude connects exclusively to that workspace through a scoped remote MCP server.
Fastio Cloud Sync connects Google Drive, Dropbox, Box, and OneDrive folders to a workspace. Sync can run one-way (mirroring source documents into the workspace as a read-only corpus for Claude) or two-way, operating on a schedule or on demand. It is never continuous, live, or real-time, giving administrators predictable synchronization windows and ensuring files are fully indexed before AI models interact with them. SharePoint libraries are reached through the OneDrive connector, while sync configurations connect directly to designated user or corporate drives across the four supported providers.
Granular Isolation Through Workspaces
The primary security advantage of this pattern is workspace-level isolation. Fastio enforces role-based permissions set per organization, workspace, and share through member roles. Permissions are never configured per folder or per file; every member of a workspace accesses its contents based on their assigned role.
To restrict Claude's access to a specific client engagement, legal matter, or engineering initiative, administrators create a dedicated workspace and synchronize only that specific folder from Google Drive or OneDrive. Even if the underlying corporate cloud drive contains thousands of confidential directories, Claude can physically access only the files synchronized into that single workspace.
Scoped OAuth and Remote MCP Connectivity
Rather than relying on local configuration files or unverified desktop bridges, Claude connects to Fastio through a remote MCP server hosted at https://mcp.fast.io/mcp/tools using the Streamable HTTP transport. Complete configuration details can be found in the Fastio MCP setup guide.
When connecting Claude to Fastio, authentication uses standard OAuth in the browser. During sign-in, Fastio presents a Review Permissions screen where the administrator or user explicitly selects the permission level:
- Read Only: Restricts Claude to searching, reading, and querying workspace documents without granting any write or modification capabilities.
- Read & Write: Enables Claude to create new files, save research notes, or update project deliverables when explicitly directed.
- Target Selection: The user explicitly designates which organizations and workspaces the connection can reach, preventing the AI model from accessing unapproved workspaces.
Built-in Hybrid Search Instead of Bulk File Pulls
When Intelligence Mode is enabled on a Fastio workspace, files are automatically indexed on arrival for hybrid search (combining full-text keyword matching, semantic meaning, and metadata values).
Instead of Claude downloading massive files over cloud APIs, Claude invokes Fastio MCP search tools. The search engine queries the indexed files and returns concise, relevant passages accompanied by source document citations. In independent connector benchmarks published at Fastio connector benchmarks, Fastio was measured the fastest and the lowest cost of the providers tested.
Auditing, Versioning, and Revocation
Governance requires continuous operational visibility. Fastio maintains a detailed activity log that records changes across the organization, tracking who uploaded, edited, moved, or deleted files, along with membership updates, permission adjustments, and share creation. It records modifications made by humans and agents alike, though it does not record read-only events such as views, previews, opens, or downloads.
Every file stored in Fastio preserves full per-file version history. If an agent with write permissions modifies or replaces a document, prior versions remain restorable at any time.
If an AI connection needs to be severed, administrators can revoke access immediately. Disconnecting requires removing the connector in Claude, opening Settings in Fastio, selecting Devices & Agents, opening Connected Devices, and selecting Revoke.
Fastio runs on cloud infrastructure partners, including Google Cloud Platform and Cloudflare, that are certified to industry-leading security standards. Data is protected with encryption in transit and at rest, role-based access controls, and detailed change tracking.
Monthly plans start with a 14-day free trial, which requires a credit card. Review complete plan allowances and seat limits on the Fastio pricing page:


Secure Claude Data Access with Isolated Workspace Sync
Connect Claude to scoped Fastio workspaces over MCP with OAuth. Sync project folders from Google Drive, Dropbox, Box, or OneDrive without exposing entire corporate drives. Monthly plans start with a 14-day free trial.
Steps to Connect Claude to a Scoped Storage Workspace
Setting up a secure storage connection between Claude and your corporate files requires only a few minutes. Follow these practical steps to configure isolated workspace sync and connect Claude using the official remote MCP endpoint:
Step 1: Designate Target Folders in Existing Storage
In your existing cloud storage provider (Google Drive, Dropbox, Box, or OneDrive), organize the documents you want Claude to access into a clean, dedicated project folder. Ensure this folder contains only documentation, specifications, or reference data relevant to the task, excluding unneeded financial sheets, personal folders, or unvetted external uploads.
Step 2: Configure Fastio Cloud Sync
Inside Fastio, create a new workspace dedicated to the project (for example, "Engineering Specifications" or "Q4 Market Research").
- Open the workspace and select Cloud Sync.
- Choose your cloud storage provider (Google Drive, Dropbox, Box, or OneDrive) and authorize the connection.
- Select the specific target folder identified in Step 1.
- Configure sync direction: choose one-way sync to create a read-only AI research library, or two-way sync if agents will save deliverables back to the shared drive.
- Set your synchronization preference to run on a scheduled interval (hourly, daily, or weekly) or run on demand.
Step 3: Enable Intelligence Mode
In your workspace settings, ensure Intelligence Mode is toggled on. Fastio will automatically scan incoming files, extract text from PDFs, presentations, spreadsheets, and Word documents, and generate hybrid search indexes. No manual vector database configuration or embedding pipeline is required.
Step 4: Add the Fastio Connector in Claude
Connect Claude directly to the Fastio remote MCP server using these exact steps:
- In Claude (web, desktop, or mobile), open Customize, then select Connectors.
- Select Add custom connector and paste the remote endpoint:
https://mcp.fast.io/mcp/tools - Select Connect. A secure browser window will open to sign in to Fastio.
- On the Review Permissions screen, choose your desired permission scope (Read Only for research and analysis, or Read & Write if Claude needs to generate files).
- Select the specific organization and workspace containing your synchronized project files, then confirm authorization.
- Return to your Claude conversation. Open the
+menu under Connectors and turn Fastio on for your chat.
Step 5: Execute Scoped Queries with Citations
Once connected, prompt Claude naturally. Rather than pulling raw files across the network, Claude uses the storage tool on /mcp/tools to search the indexed workspace.
User: What database indexing strategy is recommended for large file metadata in our architecture document?

Claude: [Invokes Fastio storage search tool with query "database indexing strategy large file metadata"]
Retrieves relevant text excerpts with file identifiers.

According to the architecture specification, metadata queries use compound primary indexes on workspace and file identifiers, combined with asynchronous full-text indexing for extracted document content.
Claude answers the question accurately using specific document passages without loading the entire engineering manual into context, preserving token allowances and preventing exposure to unrelated corporate files.
Step 6: Audit and Manage Active Connections
Maintain continuous governance by monitoring the connection over time:
- Review Changes: In Fastio, open the workspace's detailed activity log to inspect all file additions, edits, and deletions made by team members and connected agents.
- Revoke Tokens: When a project concludes or team assignments change, disconnect the integration. Remove the connector in Claude, then in Fastio open Settings, select Devices & Agents, navigate to Connected Devices, and select Revoke on the active Claude token.
Sources
References used to verify factual claims in this guide.
-
Claude inherits each user's permissions directly from the connected external service.
Frequently Asked Questions
What data can Claude Connectors access in my cloud storage?
Claude Connectors can access only the specific files, folders, and resources permitted by the connector's authentication scope and the user's account permissions. In pre-built cloud connectors like Google Drive, authorization often grants read access across the user's entire account. When using custom remote MCP connectors connected to scoped workspaces, Claude's access is restricted strictly to the designated workspace and approved tool definitions.
Does Anthropic train models on data accessed through Claude Connectors?
Anthropic does not train AI models on customer data from commercial plans (Claude Team, Enterprise, Government, Education, or API endpoints). Furthermore, raw content pulled dynamically through pre-built connectors or remote MCP servers is not used for model training across any tier. Connector data only enters training datasets on consumer accounts if a user manually copies and pastes connector output into a standard chat prompt or submits conversation feedback.
How do I restrict Claude Connector permissions to specific folders?
Standard cloud storage OAuth implementations rarely support folder-level scoping during initial connection. To enforce strict folder boundaries, organizations synchronize designated project folders from Google Drive, Dropbox, Box, or OneDrive into an isolated Fastio workspace using scheduled Cloud Sync. Claude is then connected to that specific workspace over remote MCP with Read Only permissions, physically preventing the AI from accessing the rest of the corporate drive.
Can Claude Connectors modify or delete files?
Claude Connectors can only modify or delete files if granted explicit write permissions during OAuth authorization and if the underlying MCP server exposes write tools. On Fastio's remote MCP server, administrators choose between Read Only and Read & Write permissions on the Review Permissions screen. When write permissions are granted, actions like file deletion or editing require explicit tool calls, and Fastio's per-file version history ensures every previous version remains restorable.
What is the difference between Claude pre-built connectors and custom MCP connectors?
Pre-built connectors are turnkey integrations managed directly inside Claude for popular SaaS platforms like Google Drive, Gmail, and Slack. Custom MCP connectors are external servers implementing Anthropic's open Model Context Protocol over Streamable HTTP. Custom MCP connectors allow organizations to expose proprietary internal APIs, enforce strict enterprise permission scopes, and connect persistent cloud workspaces with hybrid RAG indexing.
How does workspace sync prevent Claude from exhausting context windows?
Direct cloud drive connectors often download entire raw documents into Claude's prompt context, rapidly consuming tens of thousands of tokens and increasing latency. In contrast, synchronizing folders into an intelligent workspace auto-indexes files with Intelligence Mode. When Claude queries the workspace, the remote MCP server performs hybrid search (semantic plus full-text) and returns only relevant paragraph snippets with citations, preserving context window capacity.
Related Resources

Secure Claude Data Access with Isolated Workspace Sync
Connect Claude to scoped Fastio workspaces over MCP with OAuth. Sync project folders from Google Drive, Dropbox, Box, or OneDrive without exposing entire corporate drives. Monthly plans start with a 14-day free trial.