Google Drive API for Shared Drives: Querying, Permissions, and Corpora
Accessing files inside Google Shared Drives with Google Drive API v3 requires explicit configuration flags that differ from personal drive queries. Omitting supportsAllDrives, includeItemsFromAllDrives, or proper corpora parameters leads to empty query responses and unexpected 404 errors. This guide details how to configure API v3 parameters, manage service account permissions, and connect Shared Drive contents to agentic workflows.

Why Google Drive API Queries Fail on Shared Drives
A standard Google Drive API query pointed at a file inside an organization-owned Shared Drive will quietly return an empty list or throw a 404 File Not Found error, even when the authenticated credentials have full Manager access. The failure stems from an architectural split in Google Drive. Personal My Drive spaces and organization-owned Shared Drives use fundamentally different permission models and container hierarchies, but the API defaults to personal storage unless an engineer explicitly overrides multiple request flags.
The Google Drive API for Shared Drives requires specific query flags, notably supportsAllDrives, includeItemsFromAllDrives, and corpora settings, to access and manipulate organization-owned files located outside personal user drives.
In a personal Google Drive, every file has an explicit user account listed in its owners metadata field. Storage consumption counts against that individual user quota. Shared Drives (originally named Team Drives) decouple file ownership from individual identities. The organization owns the files, the owners field in API responses is empty, and permissions cascade down from the Shared Drive root.
When Google introduced Shared Drives, older client applications built strictly for personal drives were at risk of breaking if unexpected organization-owned items appeared in standard queries. To maintain backward compatibility, Google isolated Shared Drives behind mandatory opt-in parameters. Standard developer tutorials often show simple calls like:
results = service.files().list(q="name contains 'roadmap'").execute()
When this snippet executes, the Drive API v3 defaults the corpora parameter to 'user' and assumes supportsAllDrives and includeItemsFromAllDrives are False. The query executes only against the authenticated user personal drive. Files living inside Shared Drives are silently ignored. If the developer attempts to look up a known Shared Drive item by its exact file ID using service.files().get(fileId='...').execute(), the API returns HTTP 404. The response does not indicate that the file resides in a Shared Drive; it reports that the file does not exist.
Related guides
- How to Download Files with Google Drive API: Media vs Export MethodsDownloading files through the Google Drive API requires using files.get with alt=media for binary files or files.export...
- How to List Files with Google Drive API: Pagination, Queries, and Agent WorkspacesListing files with the Google Drive API requires using the files.list method with structured query parameters, explicit...
- How to Move Files with Google Drive API: addParents, removeParents & Shared DrivesMoving files in the Google Drive API requires calling files.update with addParents and removeParents parameters rather...
- How to Connect ChatGPT to Google Shared DrivesConnecting ChatGPT to Google Shared Drives gives teams direct conversational access to collective documentation,...
- Google Drive Resumable Upload: Architecture, Limits, and Workspace SolutionsGoogle Drive resumable upload is an HTTP protocol for transferring files larger than 5 MB in chunks, using a temporary...
- How to Download Files from Box via API: Endpoints, Tokens & LimitsDownloading files through the Box REST API requires requesting the GET /files/{file_id}/content endpoint and following...
More on this subject: Agent File and Document Workflows (325 guides)
How to Configure supportsAllDrives, includeItemsFromAllDrives, and Corpora
Querying files and folders inside Shared Drives requires configuring four distinct parameters within Google Drive API v3. Leaving even one parameter at its default value causes queries to fail or return partial data sets. Developers can verify these specifications in the official Google Drive API v3 documentation and the implement shared drive support guide.
The Query Parameter Hierarchy
Working with Shared Drives requires three core parameters on the files resource, plus an identifier parameter when scoping to a specific container:
- supportsAllDrives (boolean): Informs the API that the client application understands Shared Drive architecture. It is required on both read and write operations. Calling files.get, files.create, files.update, files.delete, or files.copy on a file in a Shared Drive without setting supportsAllDrives=True causes the API to reject the request with a 404 or 403 error.
- includeItemsFromAllDrives (boolean): Instructs search queries to include files and folders located inside Shared Drives. While supportsAllDrives signals application capability, includeItemsFromAllDrives instructs the search index to include Shared Drive objects in the returned collection.
- corpora (string): Defines the body of files evaluated by the search filter. In API v3, valid values include 'user' (personal files and direct shares), 'drive' (a single Shared Drive), 'allDrives' (personal files combined with all accessible Shared Drives), and 'domain' (files shared across the Google Workspace organization).
- driveId (string): When setting corpora='drive', you must supply the unique ID of the target Shared Drive in the driveId parameter. Omitting driveId when corpora='drive' results in an invalid argument error.
Python Implementation for Shared Drive Queries
The following implementation uses the official google-api-python-client library to authenticate and query files inside a targeted Shared Drive, as well as searching across all available drives.
from google.oauth2 import service_account
from googleapiclient.discovery import build

def get_drive_service(credentials_path: str):
    scopes = ['https://www.googleapis.com/auth/drive.readonly']
    creds = service_account.Credentials.from_service_account_file(
        credentials_path, scopes=scopes
    )
    return build('drive', 'v3', credentials=creds)

def list_files_in_shared_drive(service, shared_drive_id: str, query: str = None):
    params = {
        'corpora': 'drive',
        'driveId': shared_drive_id,
        'includeItemsFromAllDrives': True,
        'supportsAllDrives': True,
        'pageSize': 100,
        'fields': 'nextPageToken, files(id, name, mimeType, modifiedTime, size)'
    }
    if query:
        params['q'] = query
    all_files = []
    page_token = None
    while True:
        if page_token:
            params['pageToken'] = page_token
        response = service.files().list(**params).execute()
        all_files.extend(response.get('files', []))
        page_token = response.get('nextPageToken')
        if not page_token:
            break
    return all_files

def search_all_accessible_drives(service, search_term: str):
    params = {
        'corpora': 'allDrives',
        'includeItemsFromAllDrives': True,
        'supportsAllDrives': True,
        'q': f"name contains '{search_term}' and trashed = false",
        'pageSize': 50,
        'fields': 'nextPageToken, files(id, name, driveId, parents)'
    }
    return service.files().list(**params).execute().get('files', [])
When building automated ingestion workers, handle pagination using nextPageToken. Shared Drives often hold tens of thousands of items, and single-page responses cap at 1,000 files.
How Service Accounts and Permission Scopes Access Shared Drives
Configuring API flags in code is only half of the implementation. Many connection failures happen before a query runs because the authenticated credentials lack access to the Shared Drive container itself.
Service Accounts Versus User OAuth 2.0
Client applications connecting to Google Drive generally use one of two credential types:
- User OAuth 2.0 Credentials: Used for interactive desktop or web applications where human users log in through a browser. The token inherits whatever permissions that specific human user possesses in Google Workspace. If the user can open the Shared Drive in drive.google.com, an API call passing supportsAllDrives=True will succeed.
- Service Accounts: Used for server-side daemons, autonomous agents, and background sync workers. A service account operates with its own identity, represented by a generated email address like service-worker@project-name.iam.gserviceaccount.com.
The most frequent source of confusion with service accounts is the assumption that enabling the Drive API in Google Cloud grants the service account access to organization files. A newly created service account has an empty Google Drive space. It cannot see any files or Shared Drives in your Google Workspace domain unless it is granted explicit access.
Adding Service Accounts as Shared Drive Members
To grant a service account access to a Shared Drive, a Google Workspace administrator or Shared Drive Manager must add the service account email address directly as a member of the Shared Drive:
- In the Google Drive web interface, open the Shared Drive settings.
- Select Manage members.
- Enter the full service account email address.
- Assign an appropriate role and confirm.
Shared Drives support five distinct member roles, mapped to internal API capabilities:
- Manager (organizer): Can manage members, delete the Shared Drive, alter drive settings, and modify all content.
- Content manager (fileOrganizer): Can add, edit, move, and delete files inside the Shared Drive.
- Contributor (writer): Can create and edit files, but cannot delete files or move them between folders.
- Commenter (commenter): Can view files and submit comments.
- Viewer (reader): Read-only access to files and directory structure.
For read-only agents and indexing workers, assigning the Viewer role provides complete data access while preventing unintended writes or deletions.
Modifying File Permissions via API
When using the permissions resource to share documents inside a Shared Drive, the supportsAllDrives parameter remains mandatory.
def share_shared_drive_file(service, file_id: str, email: str, role: str = 'reader'):
    permission = {
        'type': 'user',
        'role': role,
        'emailAddress': email
    }
    return service.permissions().create(
        fileId=file_id,
        body=permission,
        supportsAllDrives=True,
        fields='id'
    ).execute()
Omitting supportsAllDrives=True on permissions.create, permissions.list, or permissions.delete triggers an HTTP 404 error if the target document resides inside a Shared Drive.
Connecting Shared Drives to Autonomous AI Agents and LLM Pipelines
Software teams routinely connect cloud storage to LLMs, autonomous agents, and RAG pipelines. Organization knowledge accumulates in Google Drive Shared Drives, as well as Dropbox team folders, OneDrive business repositories, Box enterprise hubs, and SharePoint libraries. Connecting autonomous agents directly to raw cloud storage APIs, however, introduces operational bottlenecks.
Operational Bottlenecks of Direct API Connectors
When an AI agent interacts with Google Drive directly through API v3, it faces practical operational limits:
- Rate Limits and API Quotas: Google Drive API enforces per-minute and per-day request quotas across each Google Cloud project. Autonomous agents exploring directory trees, polling for document changes, or reading file chunks can exhaust these quotas quickly, returning HTTP 403 Rate Limit Exceeded errors.
- Context Window Bloat and Token Inefficiency: Raw API calls return complete file streams. When an agent needs an answer from a 300-page operational manual or a complex spreadsheet, downloading the full document to extract two paragraphs burns tokens and slows execution.
- Credential Maintenance: Distributing service account private keys or managing OAuth token refresh cycles across multiple agent runtimes creates credential sprawl and security exposure.
Syncing Storage to Intelligent Workspaces
An alternative architecture separates long-term file storage from the agent retrieval surface. Organizations keep their primary files in Google Drive, Dropbox, Box, or OneDrive. Those existing folders then connect to a shared workspace designed specifically for storage for agents.
Fast.io provides Cloud Sync, which connects Google Drive, Dropbox, Box and OneDrive folders to a workspace, one-way or two-way, on a schedule or on demand. SharePoint document libraries can also connect through the OneDrive connector. Cloud Sync operates on schedule or on demand, never continuous or real-time.
+-------------------------------------------------------------+
| Existing Cloud Storage (Google Drive / Dropbox / Box)      |
+-------------------------------------------------------------+
                              |
                     Cloud Sync (Scheduled)
                              v
+-------------------------------------------------------------+
| Fast.io Workspace (Intelligence Mode Auto-Indexing)        |
+-------------------------------------------------------------+
                              |
               Remote MCP Server (Streamable HTTP)
                              v
+-------------------------------------------------------------+
| AI Agents (Claude / ChatGPT / Codex / Custom Agents)        |
+-------------------------------------------------------------+
Once files land in a Fast.io workspace, Intelligence Mode indexes the content automatically. Instead of an agent issuing recursive API queries across Google Drive folders and parsing raw document bytes, the agent queries the workspace search endpoint using full-text and semantic search.
Agents connect to Fast.io using the remote Model Context Protocol (MCP) server over Streamable HTTP:
- Claude applications and general MCP clients connect at
https://mcp.fast.io/mcp/tools. - ChatGPT and Codex custom servers connect at
https://mcp.fast.io/mcp/operations(or through the Fast.io plugin). - Coding agents like Claude Code, Cursor, and Continue connect at
https://mcp.fast.io/mcp/code.
Setup steps are documented at the Fast.io MCP setup guide and agent skill specifications at the Fast.io skill reference.
Where performance and efficiency are measured across native connectors in Claude Cowork, Fastio was measured the fastest and the lowest cost of the providers tested. The full methodology and results are published in the benchmark report.
Inside Fast.io workspaces, permissions are managed through member roles set per organization, workspace, and share. A detailed activity log records changes across the organization, including uploads, edits, moves, deletions, and share modifications.
Monthly plans start with a 14-day free trial that requires a credit card. Plans include Starter at $9.99/mo (3 seats, 250 GB, 5 workspaces, 100,000 credits a month), Business at $49.99/mo (10 seats, 5 TB, 50 workspaces, 600,000 credits a month), and Enterprise at $199.99/mo (30 seats included, 25 TB, 200 workspaces, 3,000,000 credits a month). Credits meter AI work. Storage and seats come with the plan, and credit overage is $10 per 100,000 credits. Explore complete subscription options on the Fast.io pricing page.
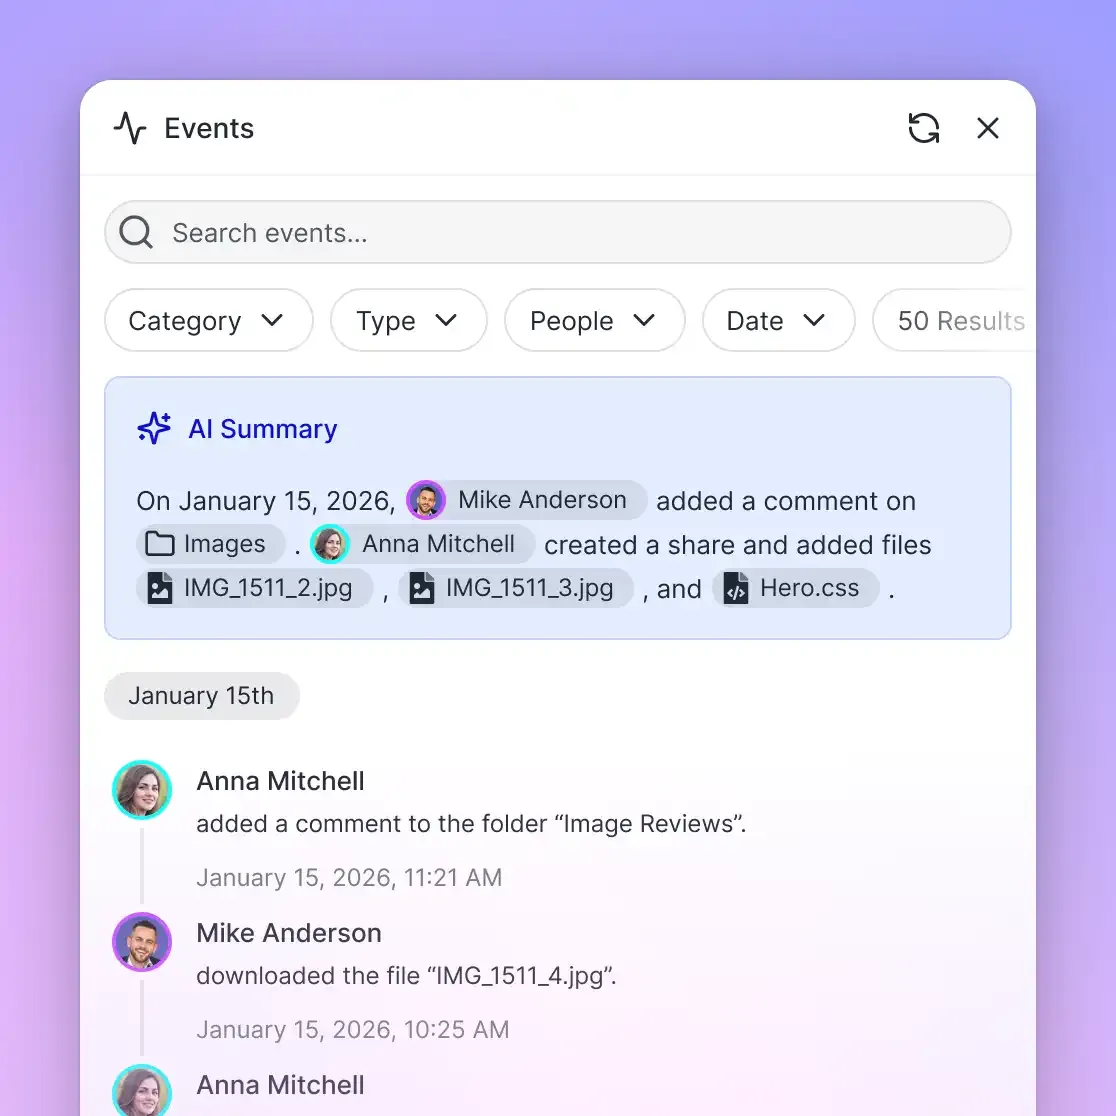


Connect Google Drive Storage to Fast.io Workspaces
Sync your organization files into persistent workspaces with automatic semantic search and remote MCP endpoints for your AI agents. Plans start with a 14-day free trial.
How to Troubleshoot Silent Query Failures and HTTP Error Codes
When building or maintaining integrations against Google Drive API v3, unexpected errors and silent query failures usually trace back to parameter omissions or misaligned permission scopes. Here is how to diagnose and resolve the most frequent failures.
HTTP 404 File Not Found on Existing Items
- Symptom: Calling files.get, files.update, or files.delete returns HTTP 404 even though the file ID is valid and visible in the web interface.
- Root Cause: The target item resides inside a Shared Drive, but the request omitted supportsAllDrives=True.
- Resolution: Add supportsAllDrives=True to the request method parameters. Every single-item method in API v3 requires this flag when operating on Shared Drive files.
Empty Query Results from files.list
- Symptom: Calling files.list returns {'files': []} despite matching files existing in the Shared Drive.
- Root Cause 1: The query omitted includeItemsFromAllDrives=True. Without this flag, the search index restricts evaluation to personal files.
- Root Cause 2: The request set corpora='drive' but did not supply driveId='
'. - Root Cause 3: The query filtered by parent folder (e.g.
'FOLDER_ID' in parents) without setting supportsAllDrives=True. - Resolution: Ensure the query combines corpora='drive', driveId='
', includeItemsFromAllDrives=True, and supportsAllDrives=True.
HTTP 400 Bad Request: Invalid Value
- Symptom: The API returns an invalidArgument error stating that parameter combinations are invalid.
- Root Cause: Combining incompatible corpora and driveId settings. For example, supplying driveId while setting corpora='allDrives' or corpora='user' triggers a 400 error.
- Resolution: Pair driveId strictly with corpora='drive'. When searching across all containers using corpora='allDrives', omit the driveId parameter completely.
HTTP 403 Forbidden: Insufficient Permissions
- Symptom: The API returns 403 Forbidden with the error message "The user does not have sufficient permissions for this file."
- Root Cause: A service account is attempting to read or write a Shared Drive where it has not been added as a member, or it holds a Viewer role while attempting an upload.
- Resolution: Check the service account email in Google Drive Shared Drive settings. Verify that it is listed under Manage members with a role appropriate for the intended action (Contributor or Content manager for uploads, Manager for deletions).
HTTP 403 User Rate Limit Exceeded
- Symptom: Batch jobs or multi-threaded agents fail during high-volume document queries.
- Root Cause: Burst requests exceed Google Drive API per-minute project limits.
- Resolution: Implement exponential backoff with jitter in API calls. For agent workflows, syncing documents to an intelligent workspace moves search and retrieval traffic off Google Drive API quotas and onto pre-indexed search endpoints.
Sources
References used to verify factual claims in this guide.
-
Google Drive API requires the supportsAllDrives parameter to handle files on shared drives.
Frequently Asked Questions
How do I access a Google Shared Drive using Google Drive API?
To access a Google Shared Drive using Google Drive API v3, configure your request with supportsAllDrives=True, includeItemsFromAllDrives=True, corpora='drive', and pass the specific Shared Drive identifier in the driveId parameter. The authenticated user or service account must also be added as a member of the Shared Drive in Google Drive.
Why does Google Drive API return 404 for files in a Shared Drive?
Google Drive API returns a 404 File Not Found error when an operation targets a file inside a Shared Drive without setting supportsAllDrives=True. In API v3, methods including files.get, files.update, and files.delete hide Shared Drive items unless the application explicitly declares support for Shared Drives.
What does supportsAllDrives do in Google Drive API?
The supportsAllDrives parameter is a boolean flag that informs Google Drive API that your application is designed to handle Shared Drive structures, including organization ownership and shared permission models. When set to True, the API permits read, write, copy, and delete operations on files inside Shared Drives.
What is the difference between corpora 'drive' and 'allDrives'?
The corpora parameter defines the search boundary for files.list requests. Setting corpora='drive' restricts the search to a single Shared Drive specified by the driveId parameter. Setting corpora='allDrives' searches across personal files and every Shared Drive accessible to the authenticated account without requiring a driveId.
Can a service account access a Google Shared Drive without domain-wide delegation?
Yes. A service account can access a Shared Drive without domain-wide delegation by adding the service account email address directly as a member of the Shared Drive in Google Drive. Assigning the service account a role like Viewer, Contributor, or Content manager grants direct access.
Does Fast.io sync with Google Drive?
Yes. Cloud Sync connects Google Drive, Dropbox, Box and OneDrive folders to a workspace, one-way or two-way, on a schedule or on demand. SharePoint document libraries can also connect through the OneDrive connector. Once connected, workspace files are indexed for search and accessible to AI agents through remote MCP connections.
Related Resources

Connect Google Drive Storage to Fast.io Workspaces
Sync your organization files into persistent workspaces with automatic semantic search and remote MCP endpoints for your AI agents. Plans start with a 14-day free trial.