Claude SharePoint Permissions: Enterprise Access Controls and Setup
Claude connects to SharePoint through Microsoft Graph delegated permissions, requiring tenant-level admin consent in Microsoft Entra ID before users can query documents. Setting up least-privilege enterprise app assignments, configuring Conditional Access exclusions for Anthropic IP ranges, and managing scoped document libraries prevent unauthorized cross-site data exposure.

How Claude Connects to SharePoint and Entra ID
When an enterprise tenant connects Claude to Microsoft 365, granting delegated access to SharePoint without configuring Entra ID admin consent and library-level scoping exposes every site collection the user can view to automated retrieval. The governance challenge is not authenticating Claude; it is preventing an AI connector with broad graph scopes from indexing sensitive corporate data across departmental sites.
Claude SharePoint permissions are the Microsoft 365 security privileges and Entra ID scopes required to authorize Anthropic's platform to access and query specific organizational SharePoint repositories. Anthropic implements this integration as a hosted proxy service. Rather than installing an agent directly onto your Microsoft 365 servers, the integration uses the Model Context Protocol (MCP) over Streamable HTTP to bridge Claude chat interfaces with the Microsoft Graph API.
When an employee asks Claude a question that requires consulting company documentation, Claude does not maintain a full background index of your corporate intranet. Instead, the connector queries Microsoft Graph on demand during active chat interactions. Microsoft Azure SDK handles an On-Behalf-Of (OBO) token exchange, validating the authenticated user identity against the tenant before executing any tool call.
Behind the scenes, connecting Claude to SharePoint introduces two distinct enterprise application registrations within your Microsoft Entra ID tenant:
- M365 MCP Client for Claude (App ID:
08ad6f98-a4f8-4635-bb8d-f1a3044760f0): Acts as the public client facing the user during browser-based OAuth authentication. - M365 MCP Server for Claude (App ID:
07c030f6-5743-41b7-ba00-0a6e85f37c17): Acts as the backend service principal that receives delegated tokens and interacts directly with Microsoft Graph endpoints.
Because Microsoft 365 treats both registrations as multi-tenant enterprise applications requesting broad organizational scopes, standard users cannot connect their accounts independently. A Microsoft Entra Global Administrator must complete a one-time consent process before anyone in the tenant can connect. Until this tenant-wide approval is established, end-user connection attempts stop at an administrative approval block.
Related guides
- Can Copilot Access SharePoint? Permissions, Libraries, and SetupMicrosoft Copilot can access SharePoint document libraries when users hold explicit read permissions through Microsoft...
- Devin AI Enterprise: Features, Security Controls, and Team SetupCognition lists Devin Teams at $80 per month plus $40 per full developer seat, while Devin Enterprise is only 'Let's...
- How to Configure Claude Code Permissions: Allow, Ask, and Deny RulesDevelopers approve 93% of Claude Code permission prompts without careful review, turning a security mechanism into...
- Claude Code SharePoint MCP: Connecting Terminal Agents to Enterprise DocsClaude Code SharePoint MCP connects Anthropic's command-line agent to Microsoft SharePoint document libraries through...
- Can Claude Access SharePoint? Permissions, Security, and WorkspacesClaude cannot browse Microsoft SharePoint without administrative setup, but teams have two primary integration paths....
- How to Fix Claude Box Permissions and Enterprise Access ErrorsClaude Box permissions govern whether Anthropic AI agents can search, read, and process managed documents in corporate...
More on this subject: Claude and Claude Code (278 guides)
What Microsoft Graph Delegated Scopes Claude Requests
The native Claude connector relies entirely on delegated permissions rather than application-only permissions. Delegated permissions mean Claude operates within the security context of the signed-in user. If a staff member does not have read access to an executive compensation site, Claude cannot retrieve documents from that site on their behalf.
However, delegated access alone does not solve the principle of least privilege in a modern corporate intranet. To allow Claude to search and retrieve files from document libraries, the connector requests two primary read scopes across Microsoft Graph:
Sites.Read.All: Grants the application permission to read documents, lists, and pages across all site collections that the signed-in user can access.Files.Read.All: Grants permission to read all files across OneDrive for Business and SharePoint libraries that the signed-in user can access.
The inherent conflict centers on the breadth of Sites.Read.All. Most corporate SharePoint environments suffer from permission sprawl. Employees frequently belong to wide Microsoft 365 Groups, department-wide communication sites, and public team channels created over years of organizational changes. When an employee connects Claude to SharePoint with Sites.Read.All, Claude gains immediate query access to every single file that user can read, including draft policies, quarterly budget sheets, and internal audits.
When write tools are enabled by an administrator, the connector also requests Files.ReadWrite.All. This scope permits Claude to create new files, overwrite content, rename folders, and move items to the recycle bin in OneDrive and SharePoint. The read and write tools exposed to Claude for SharePoint operations include:
Because write operations carry high operational impact, write tools remain blocked by default for organizations that adopted the connector prior to write tool availability. Administrators must explicitly turn them on. Even then, broad scopes like Sites.Read.All mean that IT teams must rely on administrative assignment controls rather than simple user logins to protect sensitive data repositories.
Steps to Configure Claude SharePoint Permissions and Admin Consent
To authorize Claude to communicate with your SharePoint libraries, IT administrators can choose between two deployment pathways. The choice depends on whether the Microsoft Entra Global Administrator holds an active Claude seat or requires a hands-off deployment through the Azure portal.
Option 1: In-App Consent Through Claude
If the Global Administrator maintains an account on Claude Team or Enterprise plans, the fastest approval path is in-app consent:
- Open Claude in your browser and select Customize, then open Connectors.
- Locate Microsoft 365 and select Connect.
- Authenticate using your Microsoft Entra Global Administrator credentials.
- When the Microsoft Entra permissions prompt appears, review the requested delegated permissions (
Sites.Read.All,Files.Read.All,Mail.Read,User.Read). - Check the box marked Consent on behalf of your organization and click Accept.
Once completed, the enterprise service principals are instantiated in your tenant, and standard employees can authenticate without encountering administrative consent errors.
Option 2: Manual Provisioning via Graph Explorer and Consent URLs
For enterprises where identity administrators do not have Claude accounts, administrators can provision the service principals and grant consent directly through Microsoft Graph Explorer and consent URLs.
First, sign in to Microsoft Graph Explorer (developer.microsoft.com/graph/graph-explorer) as a Global Administrator. Register the two service principals by sending POST requests to the Graph API:
POST https://graph.microsoft.com/v1.0/servicePrincipals
Content-Type: application/json

{"appId": "08ad6f98-a4f8-4635-bb8d-f1a3044760f0"}
Next, send the second POST request to register the server application:
POST https://graph.microsoft.com/v1.0/servicePrincipals
Content-Type: application/json

{"appId": "07c030f6-5743-41b7-ba00-0a6e85f37c17"}
Second, construct and visit the administrative consent endpoints in your browser, replacing {your-tenant-id} with your Microsoft Entra directory ID:
- Client App Consent:
https://login.microsoftonline.com/{your-tenant-id}/adminconsent?client_id=08ad6f98-a4f8-4635-bb8d-f1a3044760f0 - Server App Consent:
https://login.microsoftonline.com/{your-tenant-id}/adminconsent?client_id=07c030f6-5743-41b7-ba00-0a6e85f37c17
Review the requested privileges on each page and click Accept. The connection will fail until a Microsoft Entra Global Administrator approves the necessary permissions.
Enforcing Scoped User Assignment in Entra ID
By default, granting tenant-wide admin consent allows every licensed employee to connect Claude to their work SharePoint account. To restrict access to authorized pilot groups:
- Sign in to the Microsoft Entra admin center (
entra.microsoft.com). - Go to Identity > Applications > Enterprise applications.
- Select M365 MCP Client for Claude, then open Properties.
- Toggle Assignment required? to Yes and save.
- Open Users and groups, then assign only specific security groups (such as an AI Pilot User Group).
- Repeat the exact configuration for M365 MCP Server for Claude.
Setting assignment required blocks unassigned users from authenticating with Claude even if admin consent was granted across the tenant.
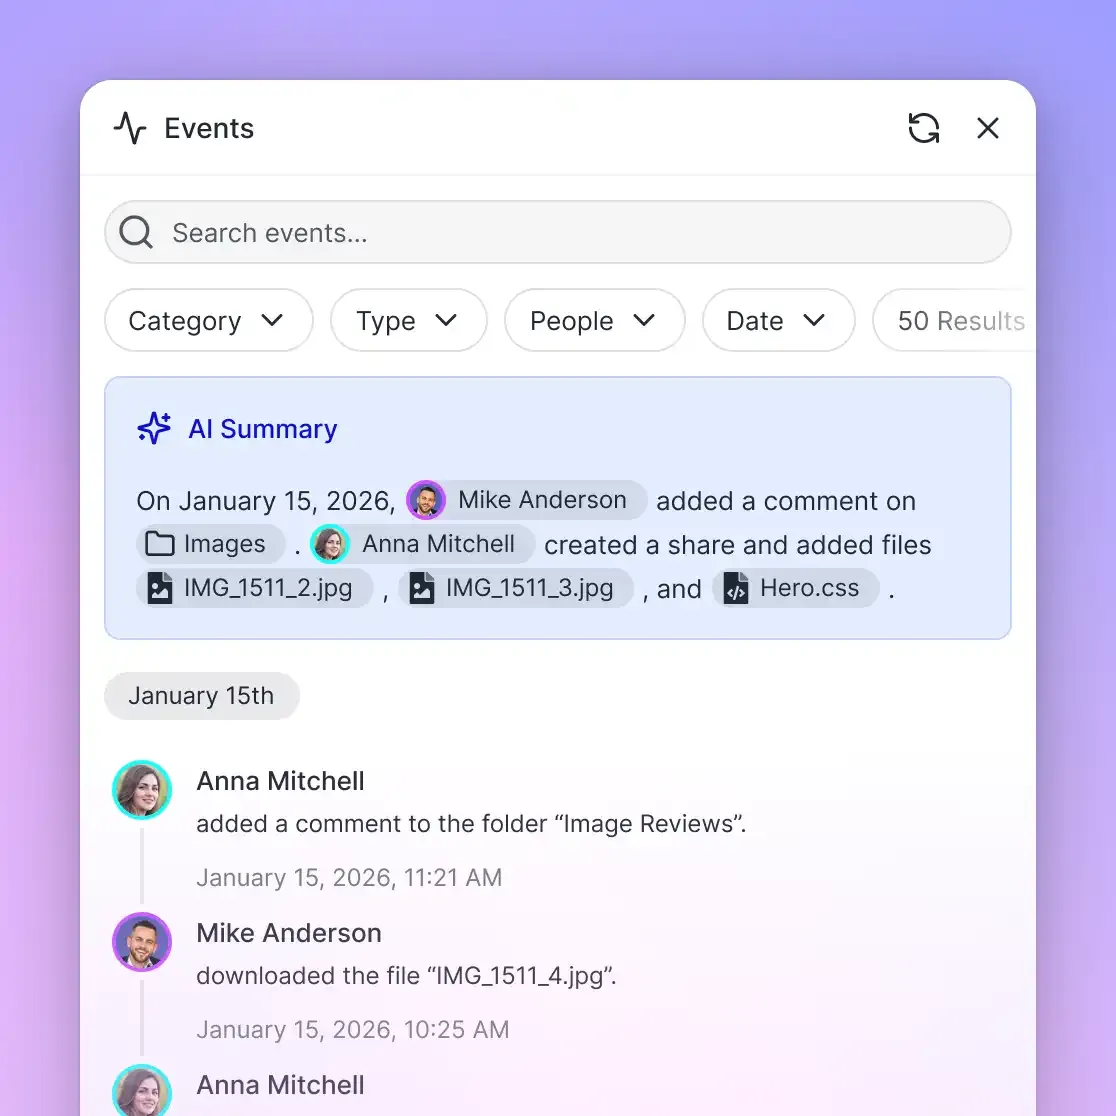


Connect Enterprise Storage to AI Agents Without Governance Risks
Sync SharePoint libraries to isolated Fast.io workspaces with role-based permissions, automatic search indexing, and unified MCP connectivity. Monthly plans start with a 14-day free trial, credit card required.
How to Resolve Conditional Access Blocks and Network Restrictions
Deploying Claude in an enterprise Microsoft 365 tenant frequently triggers unexpected blocks from Microsoft Entra Conditional Access policies. Understanding how Anthropic executes tool calls prevents unexplained authentication drops and security alerts.
When an employee connects their account, the initial OAuth sign-in occurs in their local browser. However, every subsequent query Claude performs against SharePoint originates directly from Anthropic's hosted infrastructure rather than the employee's workstation. Entra ID evaluates these backend requests as non-interactive sign-ins originating from Anthropic's public IP range:
160.79.104.0/21
This split-architecture model causes specific Conditional Access failures that administrators must resolve:
Diagnosing Common Entra ID Error Codes
To inspect connection failures, navigate to Microsoft Entra admin center, select Monitoring & health, open Sign-in logs, and switch to the User sign-ins (non-interactive) tab. Filter by the affected user identity to identify the blocking policy:
AADSTS53003(Blocked by Policy): Triggered when an organization enforces location-based Conditional Access rules, such as requiring all connections to originate from corporate IP egress points or domestic boundaries. Because Claude server calls arrive from Anthropic's CIDR block (160.79.104.0/21), the policy blocks Graph API queries.AADSTS70043(Sign-in Frequency Expired): Occurs when a Conditional Access session control requires re-authentication every few hours. Frequent re-authentication disrupts agent automation and prompts users to re-link Microsoft 365 repeatedly.AADSTS53000orAADSTS530003(Device Compliance Required): Entra ID passes the device identifier captured during the user's initial browser sign-in into downstream requests. If the browser session cannot prove device compliance (for example, using an unmanaged browser profile), Graph calls fail immediately withAADSTS53000.
Configuring Named Location Exclusions
To resolve location-based blocks without weakening network protection for human endpoints:
- In the Microsoft Entra admin center, go to Protection > Conditional Access > Named locations.
- Select IP ranges location, name it
Anthropic Claude Infrastructure, and add the CIDR block160.79.104.0/21. Leave Mark as trusted location unchecked. - Open the specific Conditional Access policy enforcing location restrictions.
- Go to Conditions > Locations, switch to the Exclude tab, and select the newly created named location.
- Save the policy. Have the affected user disconnect and reconnect the integration under Customize > Connectors in Claude.
Audit Logging and Permission Revocation
All SharePoint queries and file downloads initiated by Claude are recorded within the unified Microsoft 365 audit log. Compliance officers can query Microsoft Purview using the workload filter SharePoint to inspect operations performed by Claude service principals. Every audit entry logs the timestamp, the user identity on whose behalf Claude acted, the target site collection, and the specific file accessed.
If an organization needs to revoke access:
- Revoke SharePoint specifically: In Microsoft Entra ID, navigate to the app registration permissions and remove
Sites.Read.All. This immediately terminates Claude's ability to search SharePoint while preserving access to personal OneDrive files or Outlook email. - Revoke the integration entirely: Delete both enterprise applications (
M365 MCP Client for ClaudeandM365 MCP Server for Claude) from Microsoft Entra Enterprise Applications.
Why Scoped Workspaces Offer Better Isolation than Native Connectors
For many legal, finance, and operational teams, native Microsoft 365 connectors present significant operational tradeoffs. Broad Graph API scopes like Sites.Read.All make least-privilege scoping difficult, and querying deep SharePoint folder structures on demand can be slow when processing thousands of files. When an agent must pull whole documents over Graph API calls repeatedly, queries can hit rate limits and consume substantial prompt tokens.
Most organizations already store their working assets in SharePoint, OneDrive, Box, Dropbox, or Google Drive. Rather than exposing an entire corporate SharePoint environment to Claude with broad tenant-level permissions, teams can adopt a scoped workspace model.
Fast.io provides an architectural alternative that keeps existing SharePoint storage while establishing strict access boundaries for AI agents:
- Keep Existing Storage with Scheduled Cloud Sync: Fast.io Cloud Sync connects to Google Drive, Dropbox, Box, and OneDrive (which supports SharePoint libraries through the OneDrive connector) to synchronize designated document libraries into a dedicated Fastio workspace. Sync runs one-way or two-way, on a schedule or on demand (never continuous, live, or real-time).
- Strict Workspace Boundaries: Fast.io enforces role-based permissions set per organization, workspace, and share. Every workspace member accesses only the assets placed inside that workspace, preventing accidental data discovery across unrelated department sites.
- Automatic Intelligence and Hybrid Search: Once Intelligence Mode is enabled on a workspace, Fast.io indexes files automatically for hybrid search, combining full-text, semantic meaning, and metadata values. Claude does not need to pull whole folders across a network connector. Instead, Claude queries the indexed workspace and retrieves precise snippets with source citations.
- Structured Data Extraction with Metadata Views: With Metadata Views, teams describe required fields in natural language (such as contract parties, expiration dates, or invoice totals). Fast.io automatically generates typed columns across PDFs, Word documents, and spreadsheets without manual OCR rules. Agents can query this structured layer directly through MCP.
- Standardized Remote MCP Access: Agents connect over Streamable HTTP at
https://mcp.fast.io/mcp/tools(Claude apps and general clients) using browser OAuth. Fast.io also provides/mcp/operationsfor custom ChatGPT and Codex configurations, and/mcp/codefor coding agents. Setup instructions are detailed in the Fast.io MCP setup guide, and agents can inspect Fast.io skill documentation to explore the consolidated MCP toolset.
The performance differences between native cloud connectors and pre-indexed workspaces are documented in independent evaluations. The connector comparison is published at https://fast.io/benchmarks/ where Fastio was measured the fastest and the lowest cost of the providers tested.
Fast.io organizations run on paid subscriptions with predictable capacity:
Monthly plans start with a 14-day free trial, which requires a credit card. Extra storage beyond plan capacity is billed in cents per gigabyte each month, extra bandwidth is billed per gigabyte, and credit overages apply per block of credits.
Sources
References used to verify factual claims in this guide.
-
A Microsoft Entra Global Administrator must complete a one-time consent process before anyone in the tenant can connect.
-
The connection will fail until a Microsoft Entra Global Administrator approves the necessary permissions.
Frequently Asked Questions
What permissions does Claude require for SharePoint?
Claude requires Microsoft Graph delegated permissions to interact with SharePoint. For read access, the connector requires User.Read to authenticate the user, Sites.Read.All to discover and search site collections and document libraries, and Files.Read.All to read document contents. When write tools are enabled by an administrator, the connector also requests Files.ReadWrite.All to create, update, rename, move, and delete files.
How do I approve Claude in the Microsoft 365 Admin Center?
A Microsoft Entra Global Administrator can approve Claude in two ways. The administrator can connect Microsoft 365 under Customize > Connectors in Claude and check the box to consent on behalf of the organization. Alternatively, the administrator can register the service principals in Microsoft Graph Explorer for App IDs 08ad6f98-a4f8-4635-bb8d-f1a3044760f0 and 07c030f6-5743-41b7-ba00-0a6e85f37c17, then visit the tenant admin consent URLs to accept the permissions.
Can Claude access confidential SharePoint files?
Claude can only access SharePoint files that the authenticated user has explicit permission to read in Microsoft 365. Because Claude uses delegated permissions rather than application-wide access, it respects existing SharePoint Access Control Lists. However, because Sites.Read.All spans all sites the user can reach, Claude will index confidential files if that user has read rights, unless administrators restrict application access using Entra ID user assignments.
What is the difference between M365 MCP Client and M365 MCP Server in Entra ID?
M365 MCP Client for Claude (App ID 08ad6f98-a4f8-4635-bb8d-f1a3044760f0) handles interactive OAuth authentication in the user browser. M365 MCP Server for Claude (App ID 07c030f6-5743-41b7-ba00-0a6e85f37c17) is the backend service principal that receives delegated tokens and makes API calls to Microsoft Graph to retrieve files, search sites, and execute tool requests.
Why are Claude SharePoint requests blocked by Conditional Access policies?
While user sign-in happens in the browser, Claude server-side tool calls originate from Anthropic IP addresses (160.79.104.0/21). If an organization enforces Conditional Access policies requiring trusted corporate networks, compliance egress IPs, or strict device verification, Entra ID flags these requests as untrusted and issues error codes such as AADSTS53003 or AADSTS53000. Administrators resolve this by adding Anthropic IP ranges to an excluded Named Location.
Can administrators restrict Claude to specific SharePoint sites rather than all site collections?
Native Microsoft Graph permissions do not support scoping Sites.Read.All to individual site collections through the standard connector. To restrict Claude to specific project or matter documents, organizations can set Assignment Required on the enterprise app to limit user access, or sync specific SharePoint document libraries into isolated Fast.io workspaces where permissions are governed per workspace.
Related Resources

Connect Enterprise Storage to AI Agents Without Governance Risks
Sync SharePoint libraries to isolated Fast.io workspaces with role-based permissions, automatic search indexing, and unified MCP connectivity. Monthly plans start with a 14-day free trial, credit card required.