SharePoint Folder Permissions: Managing Unique Permissions and Access Control
Managing SharePoint folder permissions allows administrators to break permission inheritance and assign unique access control lists to specific directories. Exceeding Microsoft's recommended limit of 5,000 unique security scopes causes severe query degradation, crawl delays, and API throttling for automated connectors. Structuring permissions cleanly at the site or library level keeps enterprise data secure while enabling fast search for teams and AI agents.

Why Unique Folder Permissions Create Administrative Debt
Microsoft sets a recommended limit of 5,000 unique security scopes per list or library to maintain performance, with a supported maximum of 50,000. When organizations break permission inheritance across dozens of subfolders, they push their document repositories toward this threshold, triggering query timeouts, list view failures, and index delays that disrupt daily operations.
SharePoint folder permissions control access to specific directories within a document library, allowing administrators to inherit site-wide permissions or break inheritance to assign unique access levels to specific users, groups, or service connectors.
In a default Microsoft 365 deployment, permissions follow a strict hierarchical structure. A SharePoint site collection defines root permission levels and default security groups: Site Owners, Site Members, and Site Visitors. Every document library created inside that site inherits those exact security assignments. In turn, every folder created inside a document library inherits the library's access rules, and every file inside a folder inherits from its parent directory. This predictable inheritance chain allows system administrators to manage access centrally at the site level.
However, real-world team workflows frequently challenge this model. A department might maintain a single shared document library for project deliverables while needing to restrict financial models, contractor agreements, or personnel evaluations to a subset of internal staff. Rather than provisioning a separate document library or a dedicated SharePoint site, administrators frequently take what appears to be the path of least resistance: they break permission inheritance on specific subfolders and apply custom access control lists.
How Permission Inheritance Operates Across Sites and Libraries
Understanding the mechanism of inheritance explains why subfolder exceptions introduce technical complexity. In SharePoint Online, security is governed by Access Control Lists (ACLs) evaluated by the underlying content database. When a container inherits permissions, it does not maintain its own independent access list. Instead, it holds a reference pointer to the parent security scope.
When a user attempts to open a document or browse a directory, SharePoint checks the user's Microsoft Entra ID token against the single parent ACL. Because thousands of files and folders point to that shared scope, security evaluation is immediate. Adding a new team member to the Site Members group instantly grants appropriate read or edit access across every inherited library, folder, and file without updating individual directory records.
The 5,000 Unique Security Scope Limit and Query Degradation
The operational problems begin when an administrator clicks the command to stop inheriting permissions. The moment inheritance is broken on a folder, SharePoint severs the reference pointer. The platform duplicates the existing parent ACL and writes a distinct, unique security scope record in the database for that specific folder.
Every subsequent subfolder or file with custom permissions creates another distinct security scope. As project teams share subfolders with external vendors or restrict internal access, a document library can accumulate hundreds or thousands of unique scopes, as documented in the Microsoft Learn limits specification.
This architectural fragmentation directly impacts database performance. When a user requests a list view or executes a search query across a document library, SQL Server cannot simply check a single ACL. It must perform security trimming across every unique security scope represented in the query results.
Once a library approaches or exceeds 5,000 unique security scopes, list view rendering slows down dramatically. Users encounter the standard SharePoint List View Threshold error, which restricts views when complex permission evaluation exceeds query processing limits on large libraries. Queries fail, folder navigation stutters, and batch operations time out.
The Hidden Impact on Search Crawling and Enterprise Indexing
Beyond day-to-day user navigation, fragmented folder permissions degrade backend indexing services. Microsoft Search, enterprise search crawlers, and Microsoft 365 Copilot indexing pipelines depend on continuous evaluation of document security scopes.
During search crawls, the indexing engine must calculate the effective security descriptor for every indexed object. When permissions are inherited cleanly from the library root, the indexer assigns the parent security token to all child items in bulk. When inheritance is fragmented across deep folder trees, the crawler must pause to inspect and record discrete ACLs for every uniquely permissioned folder and file.
This overhead produces substantial crawl lag. Newly uploaded or modified documents in uniquely permissioned folders can take hours to surface in search results. For automated systems that rely on timely document discovery, this indexing delay introduces operational blind spots.
Related guides
- How to Access SharePoint Files with Microsoft Graph API and AI AgentsThe Microsoft Graph API for SharePoint provides programmatic endpoints to access sites, lists, and document libraries...
- How to Create Folders with SharePoint API: REST, Graph, and Agent WorkspacesCreating folders across SharePoint environments requires choosing between legacy REST endpoints and modern Microsoft...
- How to Connect Open WebUI to SharePoint via MCPOpen WebUI SharePoint integration connects self-hosted AI models to Microsoft SharePoint document libraries via the...
- How to Get a SharePoint API Key: Authentication and App RegistrationSharePoint does not issue traditional static API keys; programmatic access requires Microsoft Entra ID App...
- SharePoint App-Only Authentication: Entra ID Setup and Agent Storage AccessSharePoint app-only authentication enables scripts and AI agents to access SharePoint Online without user interaction....
- Connecting AutoGen Multi-Agent Systems to SharePoint: Architecture and SetupAn AutoGen SharePoint connector enables Microsoft AutoGen agent teams to authenticate against Microsoft Graph and query...
More on this subject: Agent File and Document Workflows (325 guides)
How to Configure Unique Folder Permissions in SharePoint Online
When business requirements mandate unique access boundaries on a specific directory, administrators must follow a precise procedure to break inheritance cleanly and avoid orphaned security assignments.
The following step-by-step procedure outlines how to break inheritance and configure custom permissions on a target folder within SharePoint Online:
- Navigate to the document library containing the target folder.
- Locate the folder, select the checkbox next to its name, and open the Details pane by selecting the information icon in the top-right corner (or select the three vertical dots menu beside the folder).
- In the Details pane, select Manage access to open the access overview panel.
- Scroll to the bottom of the Manage access panel and select Advanced. This opens the dedicated SharePoint permissions management console for the folder.
- In the top ribbon under the Edit tab, select Stop Inheriting Permissions. A confirmation dialog appears, warning that the folder will no longer inherit permissions from its parent.
- Select OK to confirm. SharePoint copies the current parent permissions to the folder as independent, editable role assignments.
- Select the checkboxes next to any groups or individual users who should not have access to this folder, and select Remove User Permissions in the ribbon.
- To add authorized parties, select Grant Permissions in the ribbon, enter the email addresses of the designated Microsoft Entra ID groups or users, assign their permission level (such as Read or Edit), and select Share.
- Use the Check Permissions tool in the ribbon to verify that target users possess the intended access level and that restricted accounts cannot reach the directory.
Managing and Pruning Copied Role Assignments
A frequent mistake during this procedure is failing to prune the copied role assignments. When you stop inheriting permissions, SharePoint does not present a blank slate. It creates exact duplicates of all parent groups and assigns them to the folder.
If you leave the default Site Members group attached to the folder, all site members retain access, defeating the purpose of breaking inheritance. Administrators must explicitly select and remove broad groups before adding restricted groups.
Assign permissions to Microsoft Entra ID security groups or Microsoft 365 groups rather than individual user accounts. Granting direct access to individual people scatters user names across hundreds of folders. When an employee leaves the company or changes roles, IT staff must manually locate and scrub every folder-level permission assignment, creating an administrative burden and security risk.
Restoring Permission Inheritance When Scopes Are No Longer Needed
When a project concludes or access restrictions expire, administrators should restore permission inheritance to reduce the library's total count of unique security scopes.
To restore inheritance:
- Navigate to the folder in the document library.
- Open the Details pane, select Manage access, and click Advanced to load the folder permissions console.
- In the ribbon under the Edit tab, select Delete unique permissions.
- Confirm the prompt stating that inherited permissions will be restored.
SharePoint immediately discards the unique security scope and deletes all custom role assignments applied to the folder. The directory reattaches to the parent library's ACL, instantly aligning with site-wide access rules and lowering the library's scope overhead.
Why Broken Inheritance Stalls Automated Connectors and AI Agents
While manual permission management is challenging for human administrators, it creates even greater friction for automated software connectors, enterprise sync engines, and autonomous AI agents. Understanding OneDrive integration patterns highlights how sync protocols handle nested scopes.
Modern engineering teams deploy AI agents to review code, extract structured data from contracts, analyze compliance documentation, and draft technical specifications. These agents connect to cloud storage through APIs or data connectors to retrieve corporate documents. When an agent attempts to work across a SharePoint library with heavily fragmented folder permissions, the connector's retrieval pipeline rapidly deteriorates. Deeply nested unique scopes turn simple directory sweeps into resource-intensive traversals that expose agent runtimes to severe latency and connection timeouts.
Microsoft Graph API Throttling and HTTP 429 Rate Limits
Automated connectors interact with SharePoint Online through the Microsoft Graph REST API. To determine whether an agent or service account has permission to read a given file, the connector must query file and folder access endpoints.
In a library with uniform inheritance, the connector verifies access at the library root once and proceeds to index or read files efficiently. In a library with fragmented folder permissions, the connector must recursively verify the /permissions endpoint for each distinct folder and subfolder to avoid exposing restricted content.
Microsoft Graph enforces strict per-tenant and per-application rate limits. When an automated connector issues hundreds of rapid permission-checking calls during a recursive directory crawl, Microsoft Graph triggers request throttling.
The API responds with HTTP status code 429 (Too Many Requests) and provides a Retry-After header instructing the application to pause execution. For an interactive AI agent running in Claude Code, Cursor, or an autonomous workflow, hitting an HTTP 429 pause halts the entire reasoning loop. The agent must wait for the throttling window to reset, leading to request timeouts and degraded responsiveness.
Security Drift, Direct Sharing Links, and Orphaned Access
A related risk in SharePoint environments is security drift caused by direct sharing links. When end users use the Share button on a folder in the web interface and generate a Specific People link, SharePoint quietly breaks permission inheritance behind the scenes.
Each sharing link creates an implicit unique security scope. Over months of standard collaboration, an apparently organized document library can accumulate thousands of hidden, one-off permission exceptions.
This invisible fragmentation creates severe security vulnerabilities:
Orphaned Permissions. When team members change departments, their direct sharing link permissions remain active on nested subfolders indefinitely because site administrators have no single dashboard displaying all nested link scopes.
Accidental Over-Permissioning. If an administrator later attempts to reorganize folder structures or moves a folder to a new location, inherited permission recalculations can fail or behave unexpectedly, exposing confidential files to unauthorized users.
Incomplete Agent Retrieval. If a service principal or agent identity lacks access to an intermediate parent folder but has access to a nested child folder, standard directory traversal APIs will fail to discover the nested documents, causing the agent to return incomplete answers.
Architectural Strategies for Clean Access Boundaries
To avoid the performance degradation, API throttling, and security drift associated with unique folder permissions, enterprise architects recommend designing structural boundaries rather than relying on folder-level access control lists. Adopting dedicated cloud workspaces or discrete libraries isolates data cleanly.
By establishing clear separation of concerns at the site and library levels, organizations keep their data secure while maintaining optimal system performance.
1. Separate Document Libraries for Discrete Access Groups
Instead of creating a single shared library with restricted subfolders, provision multiple document libraries within the same SharePoint site. For example, a project site can contain a General Documentation library (inheriting site-wide team permissions) and a Restricted Financials library (with library-level permissions restricted to project leads).
A document library represents a single security scope. No matter how many thousands of folders and files reside inside it, the entire container shares one ACL. This architecture prevents database scope exhaustion while making permissions obvious to end users.
2. Dedicated Team Sites with Microsoft 365 Groups
When access boundaries align with distinct operational groups, such as HR, Legal, or Executive Leadership, create dedicated SharePoint team sites. Each site connects to an independent Microsoft 365 Group, providing clean identity boundaries.
Separating content across dedicated sites prevents accidental cross-pollination of permissions, simplifies auditing, and eliminates the risk of an inheritance break exposing sensitive records.
3. Metadata and Filtered Views Instead of Deep Folder Trees
Much of the impulse to create complex folder hierarchies stems from a desire to organize content by category, client, or status. However, deep folder nesting combined with permissions is the primary driver of administrative complexity.
SharePoint provides managed metadata, choice columns, and filtered views. By tagging files with metadata attributes (such as Department, Confidentiality Level, or Document Type), users can filter and sort files dynamically. When access must be restricted, apply permissions to the library or site containing that class of metadata rather than creating bespoke subfolders.
Comparing Permission Models Across Storage Architectures
The operational differences between folder-level permissions, dedicated libraries, and synced cloud workspaces illustrate why structural isolation delivers superior reliability:


Connect SharePoint Document Libraries to Autonomous AI Agents
Sync Microsoft 365 libraries to an intelligent cloud workspace and give your AI agents fast, token-efficient semantic search through remote MCP. Monthly plans start with a 14-day free trial that requires a credit card.
Connecting SharePoint to Autonomous Agents Through Fastio Workspaces
Many enterprises cannot simply abandon their existing SharePoint repositories to fix permission bottlenecks. Corporate governance, compliance policies, and existing employee habits dictate that Microsoft 365 remains the core system of record. Exploring dedicated Fastio AI features provides a path forward without compromising security.
The challenge arises when organizations need autonomous AI agents, coding assistants, and automated pipelines to interact with these files. Pointing an AI agent directly at raw, permission-fragmented SharePoint libraries forces the agent into slow directory traversals, frequent Graph API rate limits, and excessive token consumption. An effective operational approach bridges existing enterprise storage with an intelligent cloud workspace designed for agentic workflows.
Cloud Sync and Pre-Indexed Hybrid Search
Instead of forcing an AI agent to crawl live SharePoint REST APIs, teams use Fastio to bridge the gap. Cloud Sync connects Google Drive, Dropbox, Box and OneDrive folders to a workspace, one-way or two-way, on a schedule or on demand. SharePoint document libraries connect through the OneDrive connector.
The synchronization engine mirrors designated document libraries into a Fastio workspace without requiring custom API integration scripts. Once documents land in the workspace, Intelligence Mode automatically indexes the files for hybrid search, combining full-text keyword retrieval with semantic vector search.
When an AI agent needs information to complete a task, it does not download multi-megabyte Office documents or evaluate complex nested folder ACLs. Instead, the agent executes targeted search queries against the pre-indexed workspace, receiving precise text passages with source document citations.
While SharePoint was not included in Claude Cowork connector benchmarks, independent testing published at published connector benchmarks measured Fastio as the fastest and lowest cost of the providers tested. By shifting synchronization and indexing to the cloud workspace layer, agents avoid traversing directory trees and downloading whole documents over live API calls.
Role-Based Permissions and Isolated Agent Workspaces
Fastio simplifies permissions by setting role-based access per organization, workspace, and share through member roles, rather than maintaining complex access controls at the folder or file level. Every workspace member accesses the workspace according to their assigned role.
When an enterprise needs to grant an AI agent or an external partner access to specific documentation, administrators do not break folder inheritance. Instead, they provision a dedicated workspace containing only the relevant synced files, or generate a branded share link.
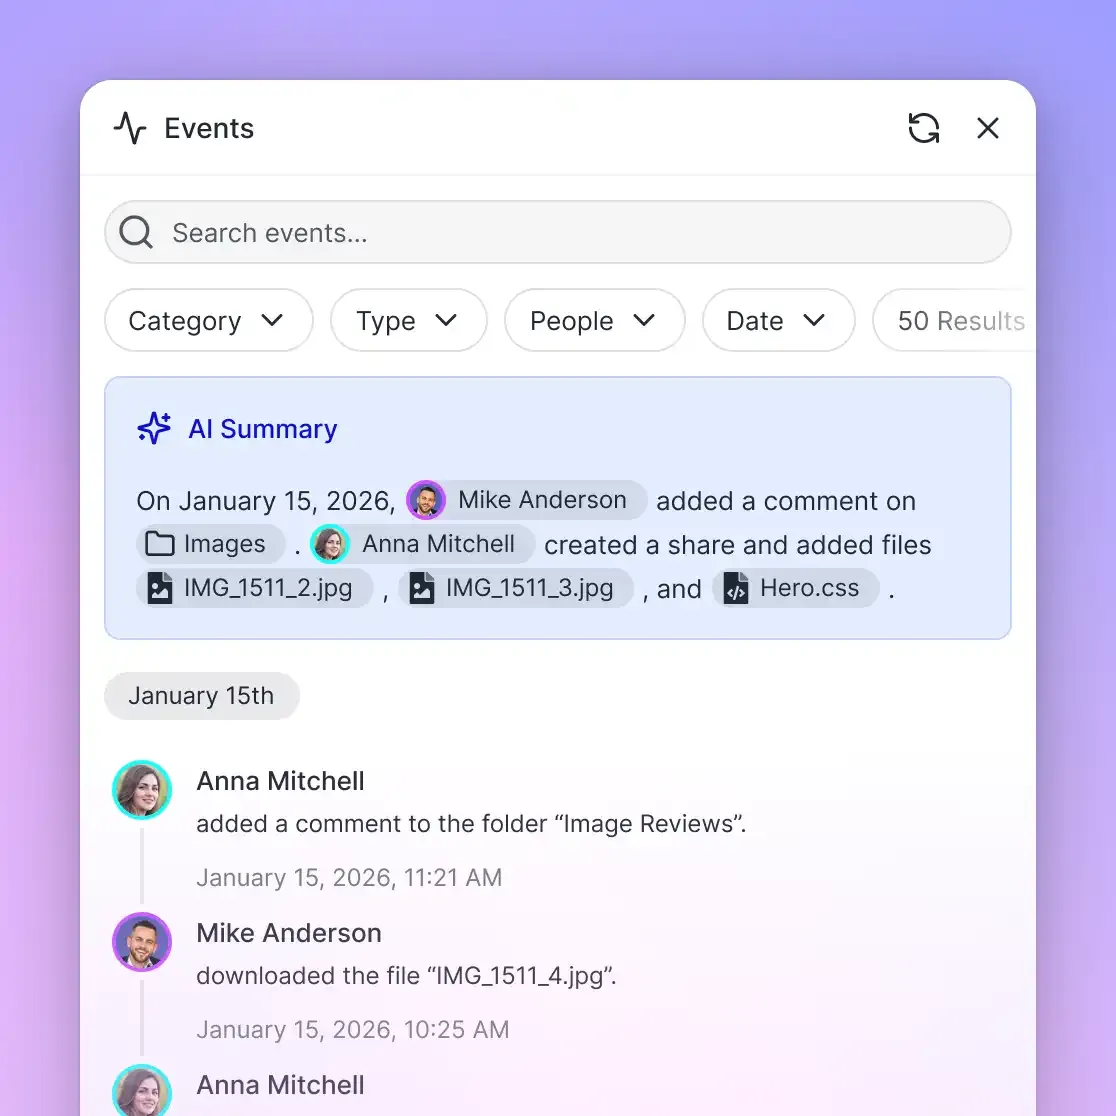
External stakeholders can view or upload documents through durable or expiring shares without requiring individual user accounts or consuming organization seats. Furthermore, Fastio tracks all modifications, uploads, and deletions in a detailed activity log, giving security teams a clear record of changes made by human members and automated agents alike.
Connecting Developer Agents via Remote Streamable HTTP MCP
Developers connect autonomous agents running in Claude Code, Cursor, Claude Cowork, Codex, or custom frameworks to Fastio using the Model Context Protocol. Full configuration instructions are available in the MCP setup documentation.
Fastio hosts a remote MCP server over Streamable HTTP. To connect an agent, developers configure the remote endpoint corresponding to their client type:
For general AI assistants and Claude applications:
https://mcp.fast.io/mcp/tools
For coding agents in IDEs or terminals (such as Claude Code, Cursor, or Gemini CLI):
https://mcp.fast.io/mcp/code
For ChatGPT and Codex environments:
Install the Fastio plugin directly from the plugin directory, or configure https://mcp.fast.io/mcp/operations as a custom MCP server.
Through these standardized endpoints, agents call search and retrieval tools natively. A developer agent can query internal API specifications or architectural diagrams stored in SharePoint, retrieve the exact technical requirements, and write verified code without leaving the editor.
Monthly plans start with a 14-day free trial that requires a credit card. Review complete plan details on the Fastio pricing page:
Sources
References used to verify factual claims in this guide.
-
Microsoft sets a recommended limit of 5,000 unique security scopes per list or library to maintain performance, with a supported maximum of 50,000.
Frequently Asked Questions
How do I set permissions on a specific folder in SharePoint?
To configure permissions on a specific folder in SharePoint Online, navigate to the document library, select the folder, open the Details pane by selecting the information icon, and choose Manage access. Select Advanced to open the permissions management page, choose Stop Inheriting Permissions in the ribbon, and confirm the dialog. Once inheritance is broken, remove existing groups that should not have access and use Grant Permissions to assign specific users or security groups with Read or Edit permissions.
What happens when you break permission inheritance in SharePoint?
Breaking permission inheritance creates a unique security scope and a distinct Access Control List for that specific folder in the SharePoint content database. The folder stops inheriting subsequent permission changes from its parent document library or site. All files and subfolders within that directory inherit its new unique permissions unless their inheritance is also broken. Accumulating thousands of unique scopes degrades library query performance and search indexing.
Can you restrict a subfolder in SharePoint without breaking inheritance?
In native SharePoint Online architecture, you cannot restrict access to a subfolder without breaking permission inheritance. Because permissions flow downward hierarchically, any user or group with access at the library level automatically inherits access to every nested subfolder. The recommended best practice is to move sensitive documents into a separate document library or dedicated team site with its own distinct permission boundary.
How do unique folder permissions affect Microsoft Graph API sync and search crawlers?
Search indexers and automated API connectors must evaluate Access Control Lists for every unique security scope encountered during directory traversal. When a document library contains hundreds of broken folder permissions, automated connectors must execute separate API calls to verify permissions for each item. This recursive checking frequently triggers Microsoft Graph API rate limits with HTTP 429 throttling and causes significant indexing lag.
How can AI agents query SharePoint documents without encountering folder permission bottlenecks?
Rather than pointing AI agents directly at raw SharePoint REST APIs, organizations can synchronize document libraries into an intelligent Fastio workspace using Cloud Sync on a schedule. Once synced, Intelligence Mode indexes the content for hybrid semantic and keyword search. AI agents query the workspace through the remote Fastio MCP server, retrieving exact text passages without traversing folder trees or making live calls against SharePoint quotas.
Related Resources

Connect SharePoint Document Libraries to Autonomous AI Agents
Sync Microsoft 365 libraries to an intelligent cloud workspace and give your AI agents fast, token-efficient semantic search through remote MCP. Monthly plans start with a 14-day free trial that requires a credit card.